Mohammad Arif
I turn security findings into scalable engineering controls.
Product security engineer with 5+ years of experience securing web, API, mobile, cloud, and software delivery systems. I combine hands-on assessment with threat modeling, DevSecOps automation, and developer enablement—and apply that foundation to adversarial ML and secure AI product design.
What I bring
I take ownership from investigation through implementation and validation—building practical controls, partnering closely with engineers, and using research to improve how products are defended.
End-to-End Engineering Ownership
Own security problems from threat modeling and hands-on testing through control design, implementation support, validation, and measurable follow-through.
Hands-on Product Defense
Build and validate safeguards across web, APIs, mobile, cloud, CI/CD, and identity-abuse scenarios while working directly with product and engineering teams.
Research into Practice
Prototype and evaluate AI/ML security, agentic penetration testing, model-abuse, and automated-analysis techniques—then translate the findings into practical controls.
Experience
A track record of improving coverage, reducing risk, and building practical security programs inside high-growth product environments.
- Implemented security controls across product features and engineering workflows.
- Reviewed and validated existing controls, identified security gaps, and recommended remediation priorities.
- Built machine-learning models and analyzed security data to strengthen bot and account-takeover (ATO) protection.
- Explored agentic penetration-testing workflows to improve the scale and repeatability of security validation.
- Designed and implemented security review processes that improved coverage across 50+ repositories.
- Expanded secure code coverage through SAST/DAST automation in CI/CD pipelines.
- Reduced remediation time by leading web, API, and mobile assessments with direct developer partnership.
- Strengthened AWS security posture across IAM, S3, and network configurations.
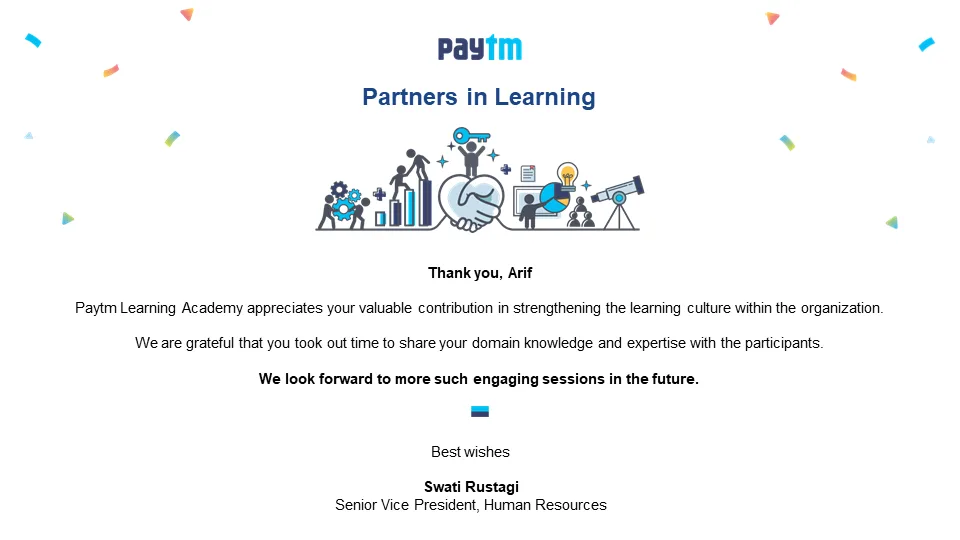
- Upskilled 100+ engineers through secure coding workshops and CTF-style learning.
- Built SSDLC and Security Champion programs to embed security from design stage onward.
- Led threat modeling and architecture reviews for critical, high-traffic applications.
- Delivered secure coding training aligned to real development workflows and OWASP risks.
- Managed bug bounty and vulnerability disclosure workflows at scale.
- Performed web, API, mobile, and network security assessments on customer-facing applications.
- Drove faster remediation through vulnerability triage, dashboards, and security playbooks.
- Partnered with engineering and DevOps to secure pipelines and reduce insecure deployment patterns.
- Conducted security testing across 30+ applications with focus on high-impact findings.
- Built Jira-based workflows and dashboards to track remediation and SLA progress.
Selected security engineering projects
Practical tooling and programs built to move security earlier in delivery, increase visibility, and make secure decisions easier for engineers.
DevSecOps Automation & Tooling
- Integrated Checkmarx SAST into CI/CD, blocking merges when high- or critical-severity findings were detected.
- Automated SCA-to-Jira reconciliation so resolved dependency findings close without manual triage.
- Created repository lifecycle guardrails that detect new repositories and enforce baseline controls from day one.
- Built a GitHub Actions auditor for insecure workflow and software-supply-chain patterns.
Cloud Security & Attack Paths
- Developed offensive tooling to demonstrate AWS SNS and SQS abuse scenarios.
- Built a Neo4j-based detector that maps cross-account attack paths within an AWS Organization.
- Created a vulnerable AWS lab for hands-on exploitation of IAM and cloud misconfigurations.
- Threat-modeled delivery pipelines and embedded preventive controls across CI/CD workflows.
AI & ML Security Research
- Built an interactive black-box attack lab around a deployed fraud-detection model, enabling users to probe and infer decision boundaries.
- Created an AI-SAST benchmark covering vulnerable business logic and OWASP-style flaws for objective scanner comparison.
- Publish practical research through the 100 Days of AI Security playbook.
Visibility & Developer Enablement
- Unified Jira, bug-bounty, and endpoint telemetry into one security-posture dashboard.
- Built a self-service testing portal that creates correctly formatted and routed security-review tickets.
- Created CTFs and vulnerable-versus-secure code labs used to train more than 100 engineers.
- Authored Security Champion and shift-left playbooks that enabled teams to self-serve common security work.
Technical depth & AI security focus
A product-security foundation spanning application, cloud, and delivery systems—extended into the security of AI-enabled products.
Core areas
AI/ML Security Direction
I apply my background in product security, offensive testing, cloud security, and secure SDLC to adversarial machine learning, model-abuse scenarios, and secure-by-design approaches for AI-enabled products.
I document this journey publicly through my 100 Days of AI Security playbook.
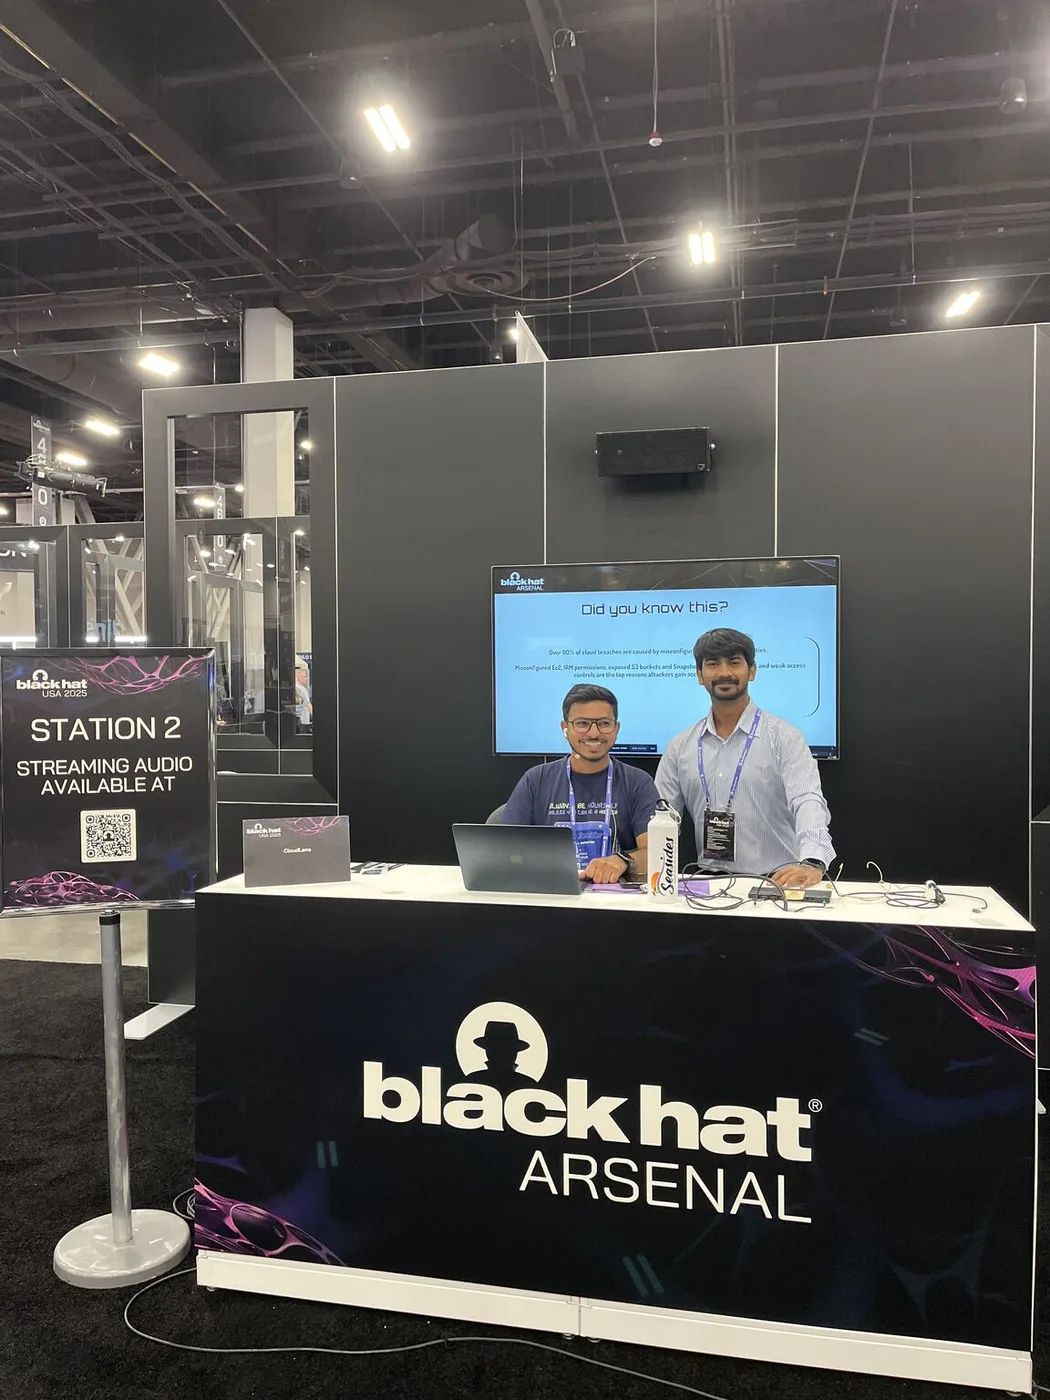
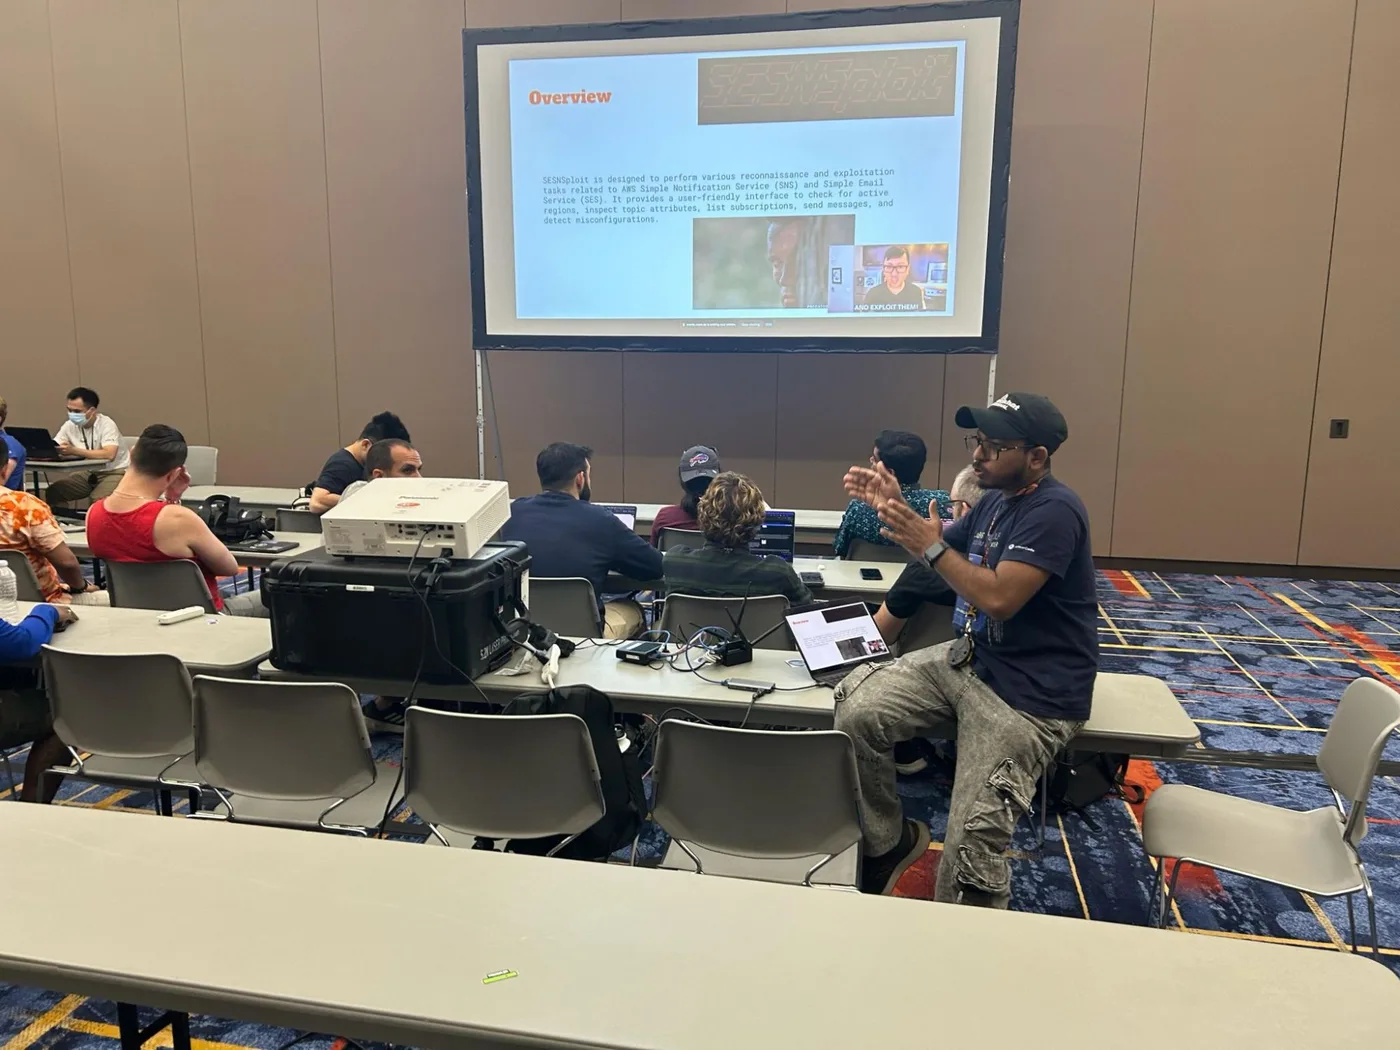
Talks & community presence
I don’t just practice security — I teach, demo, and contribute to the communities that shape it.
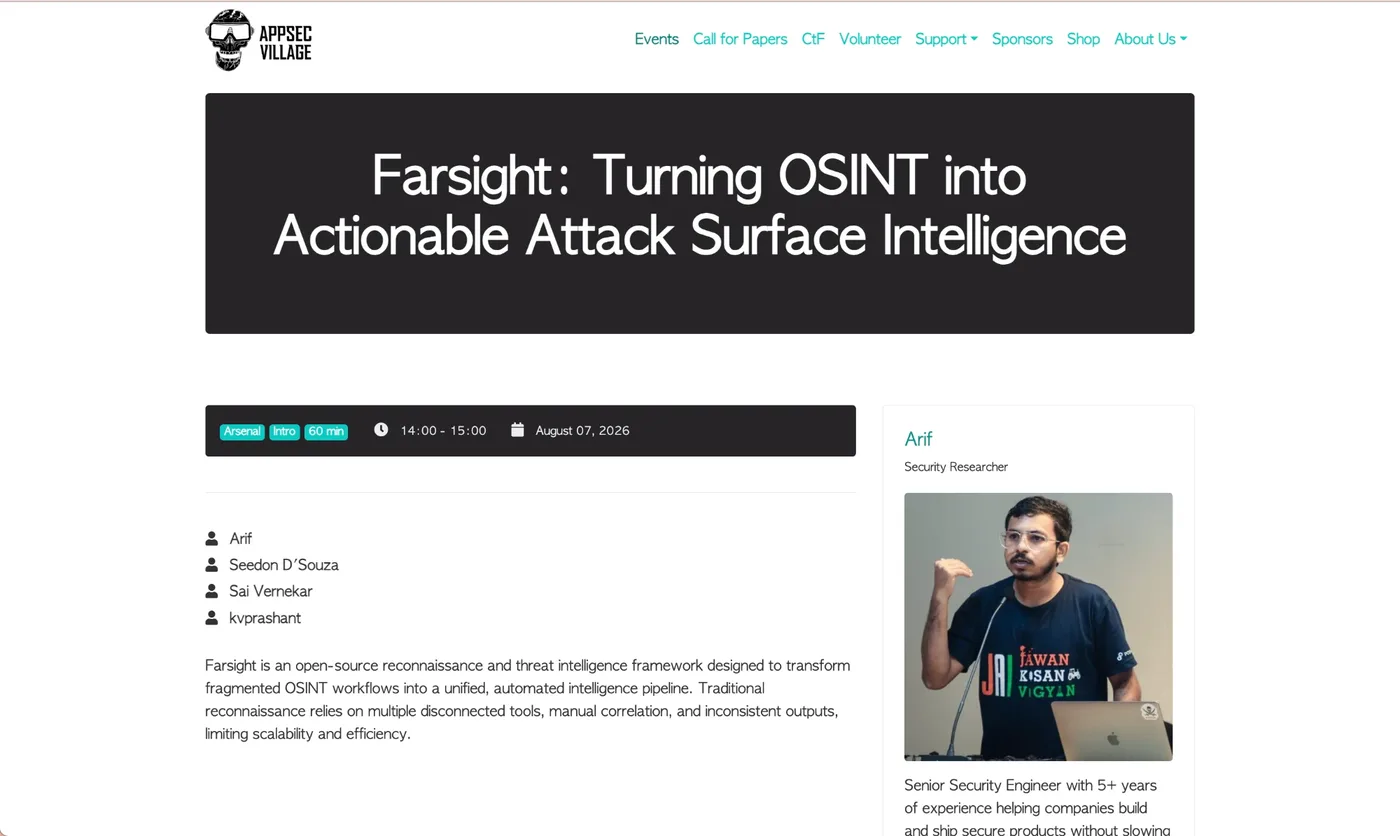
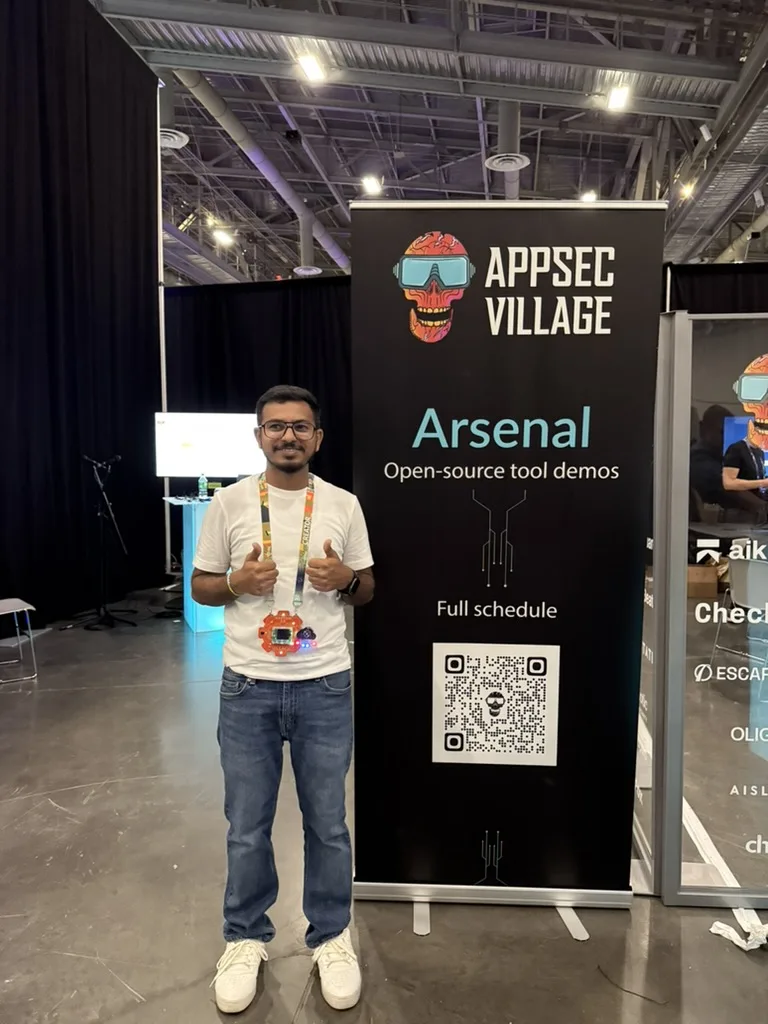
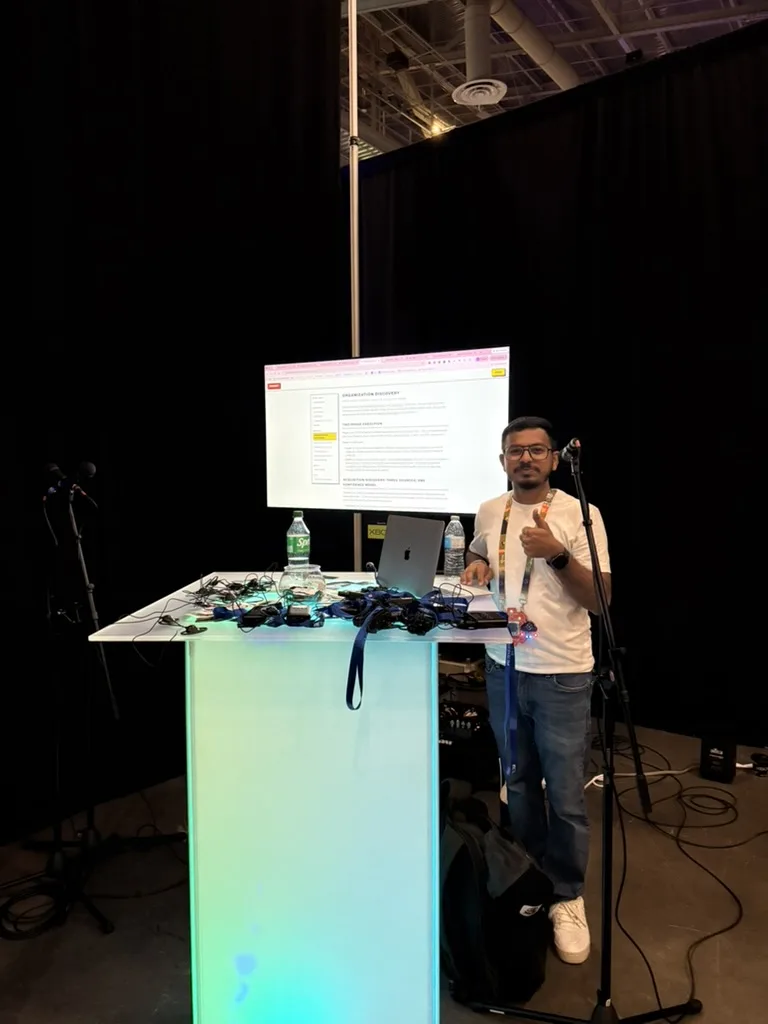
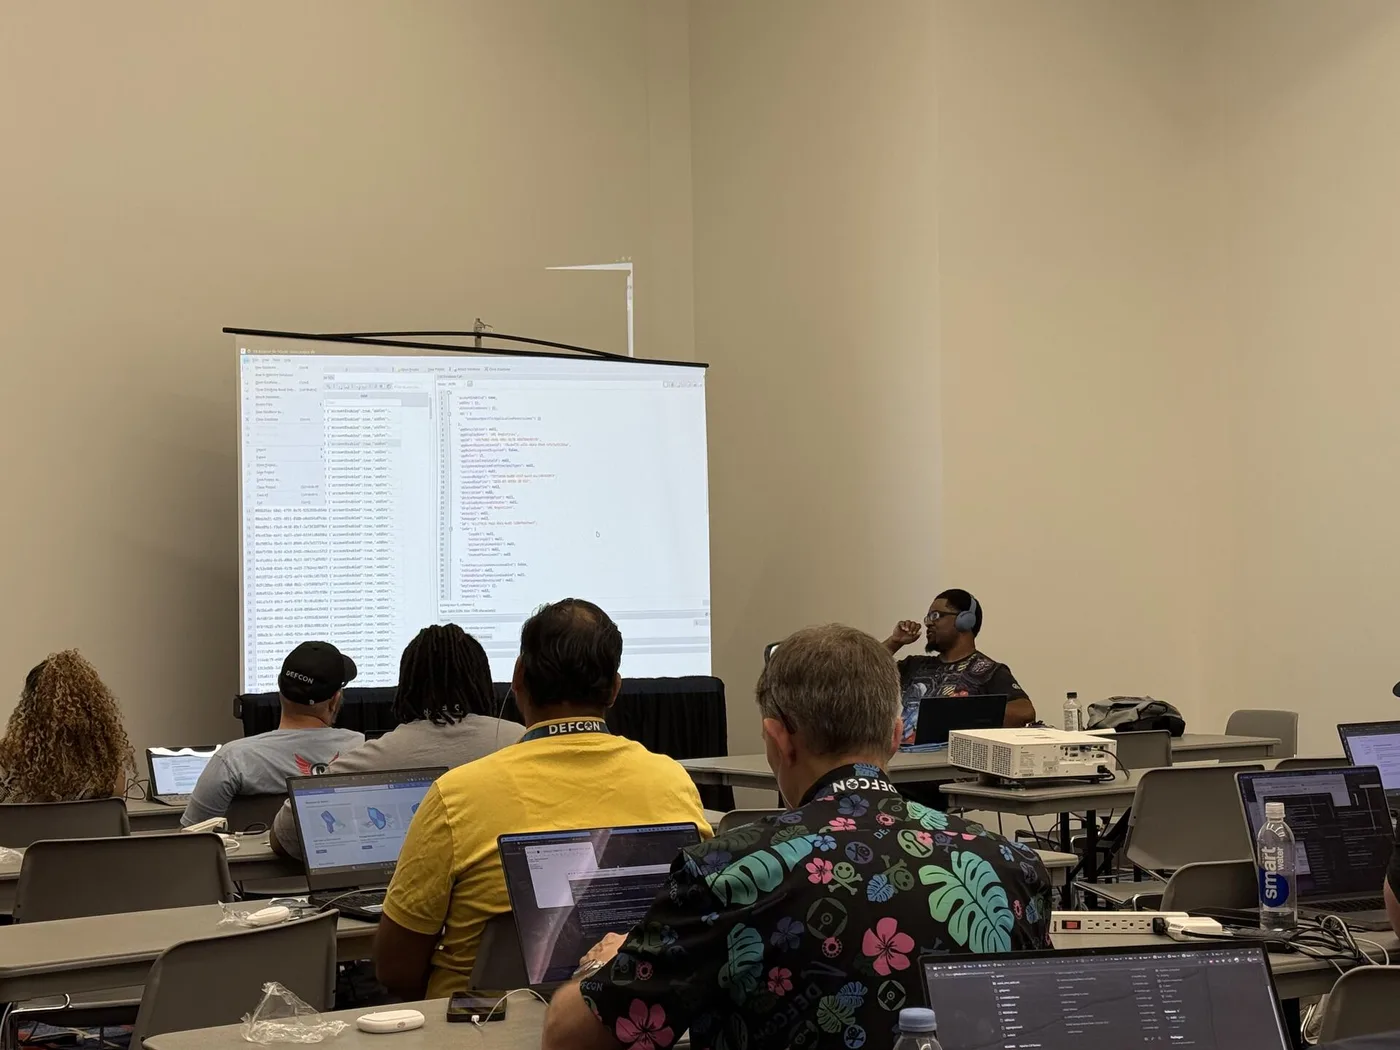
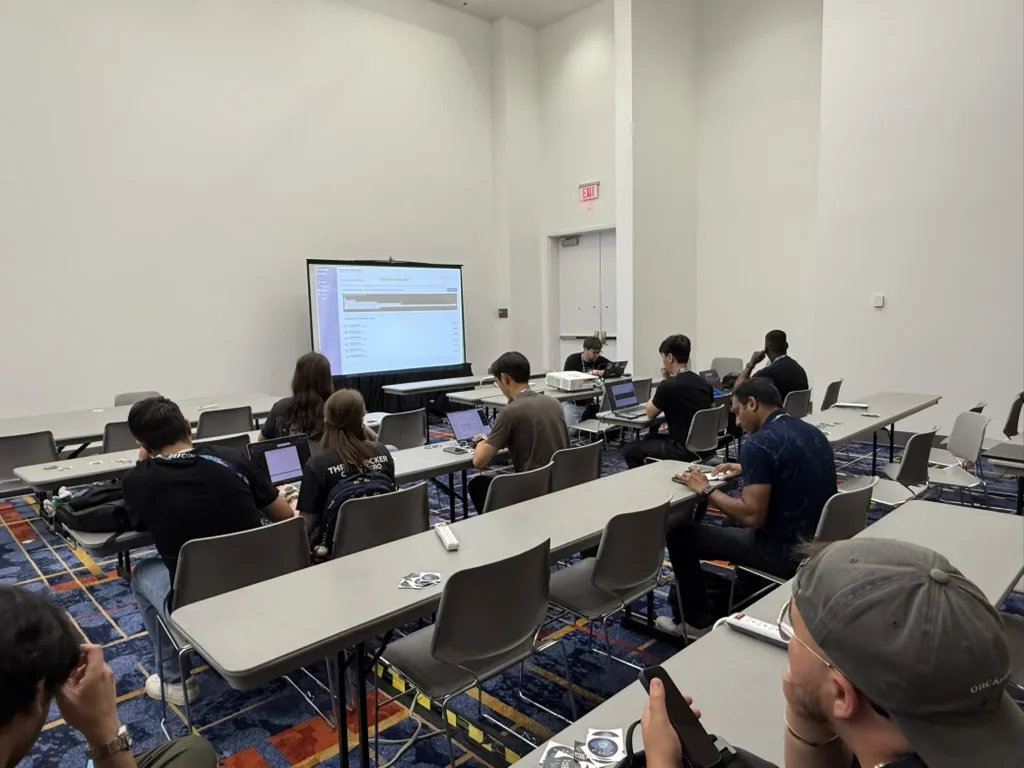
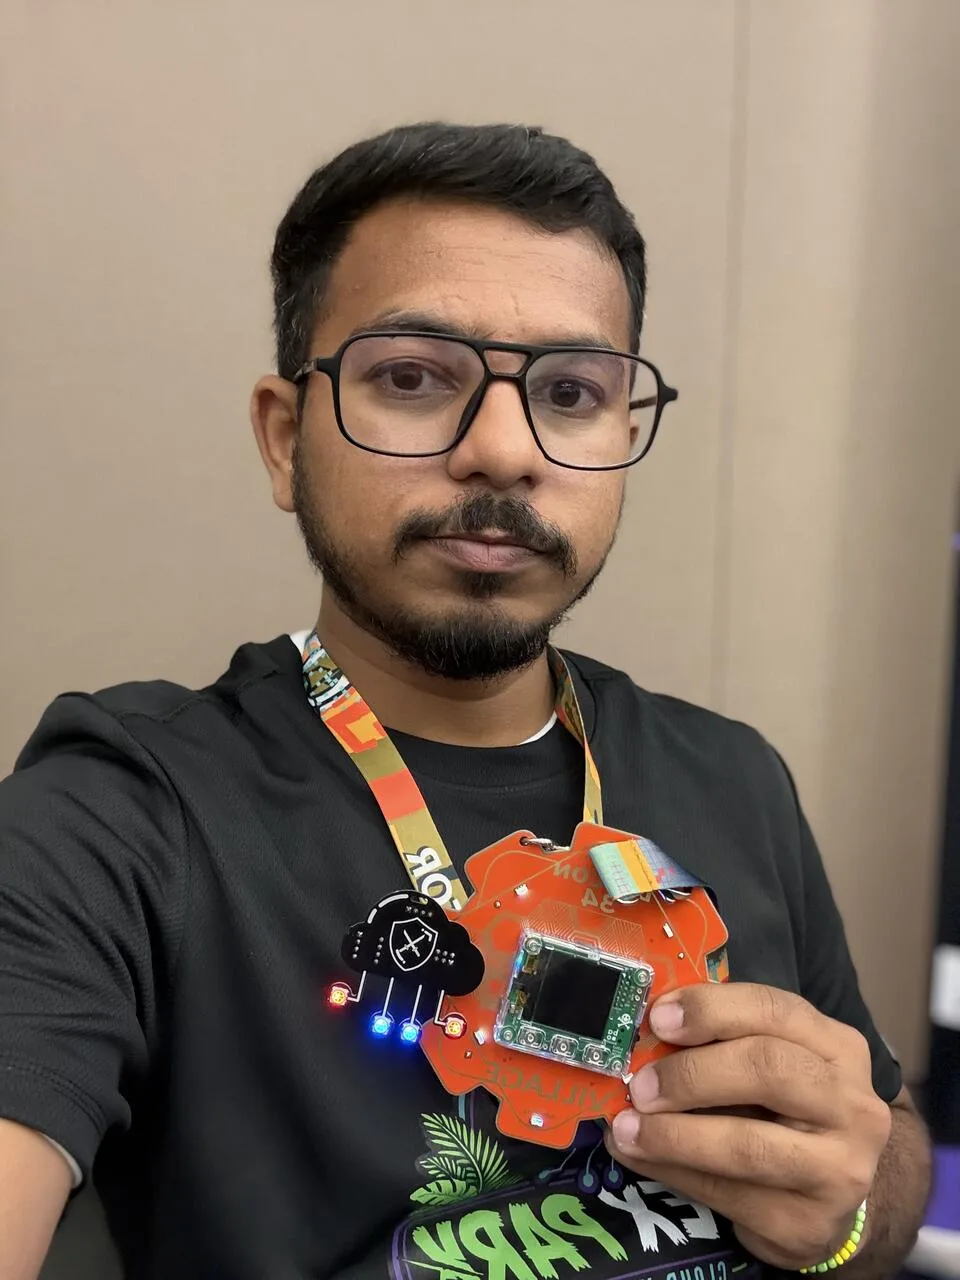
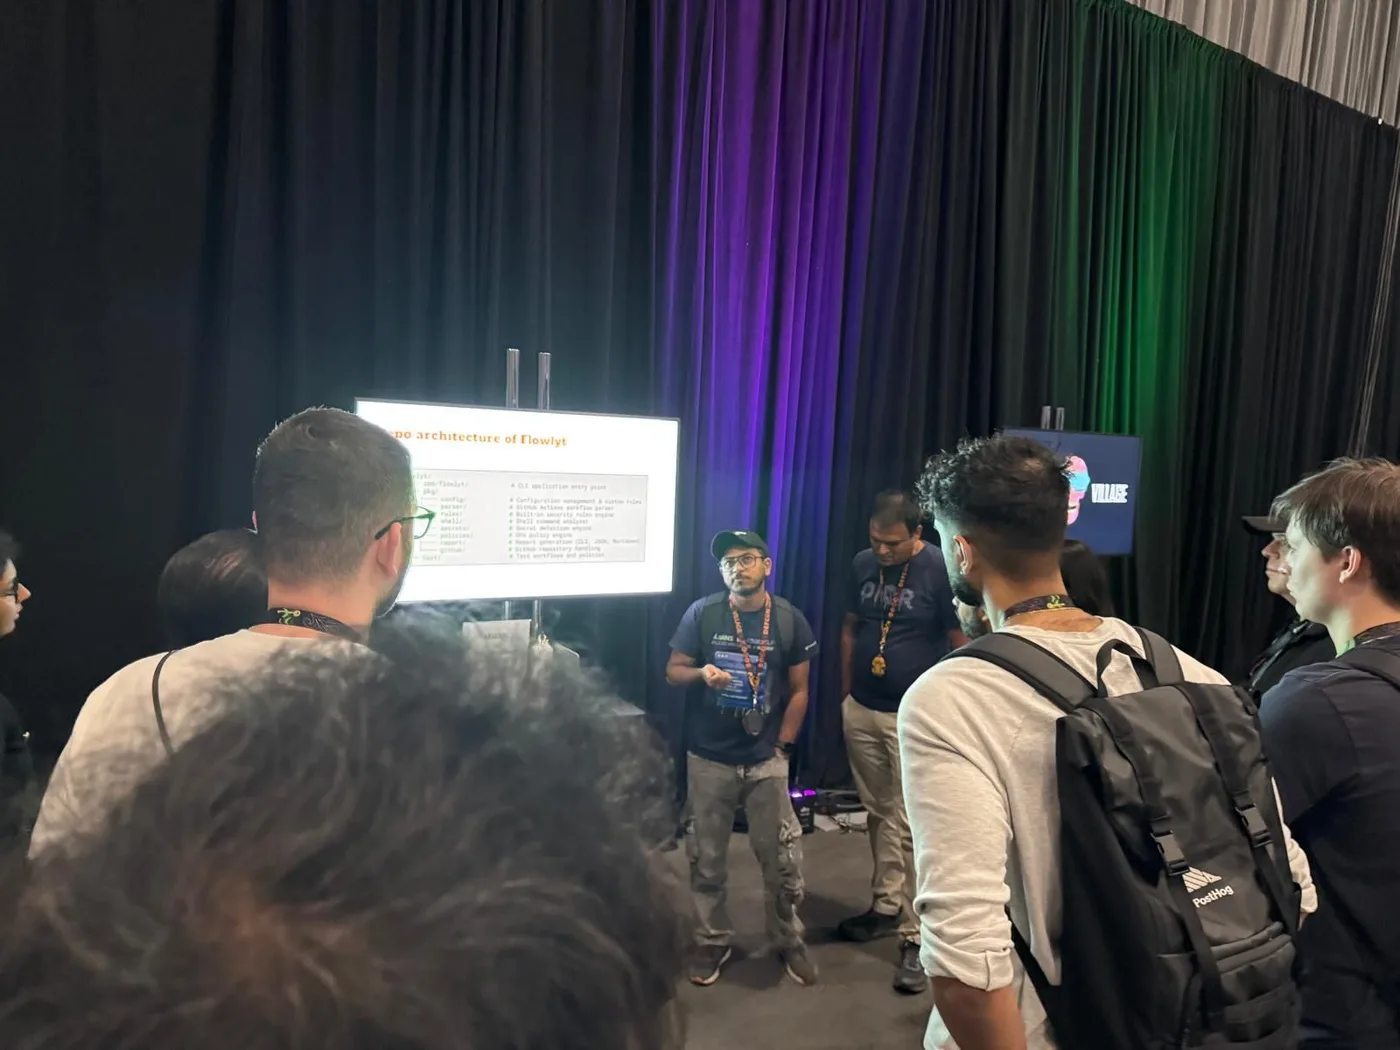
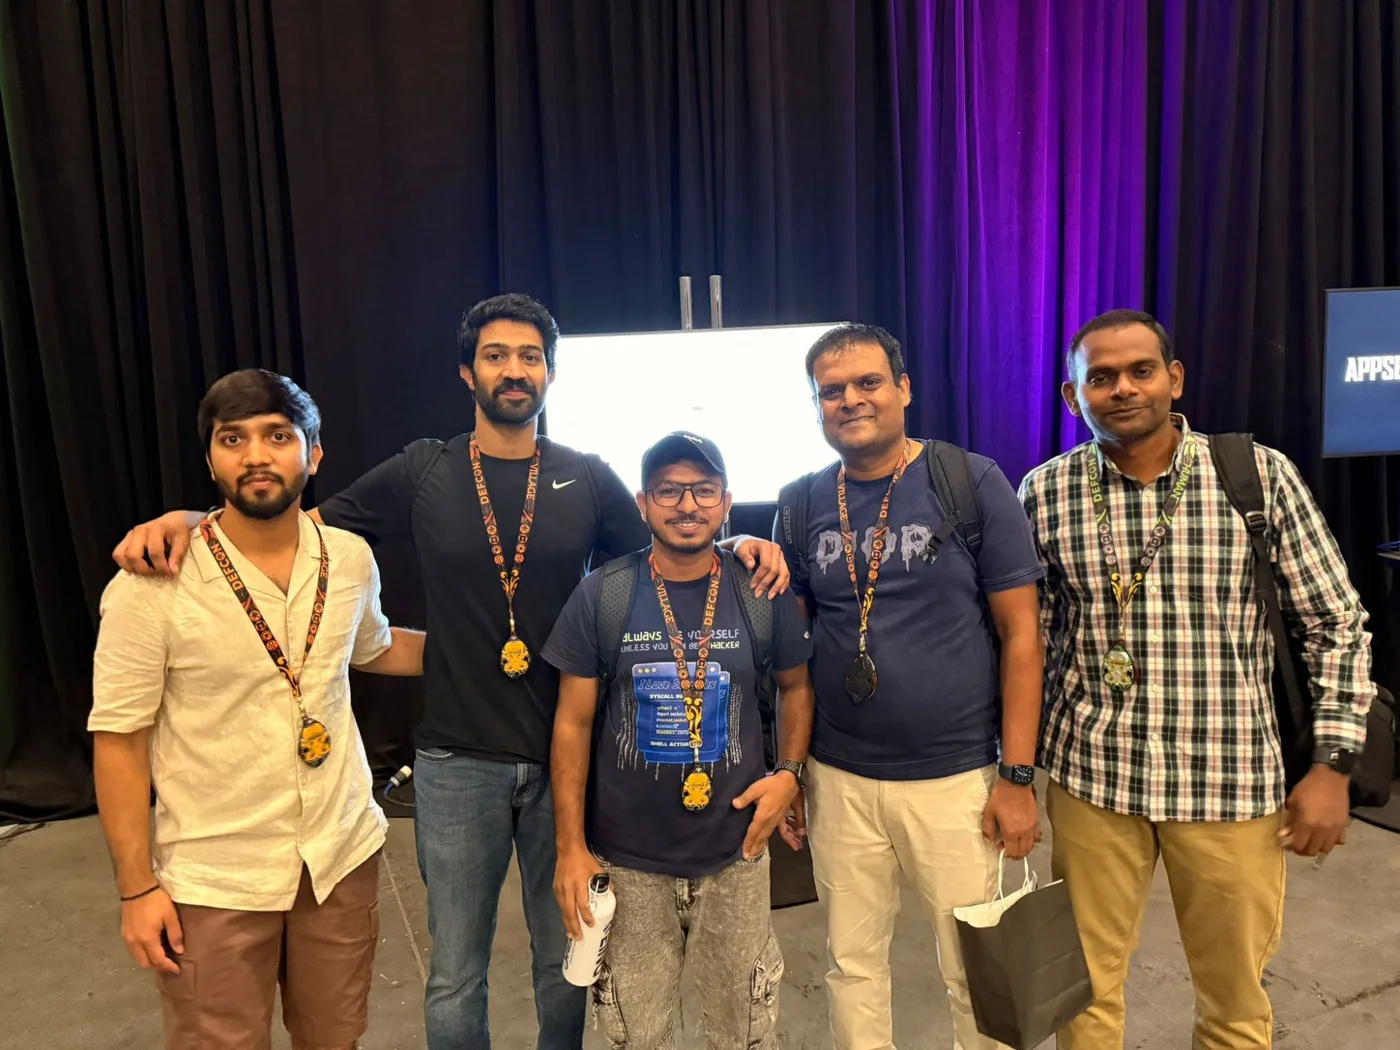
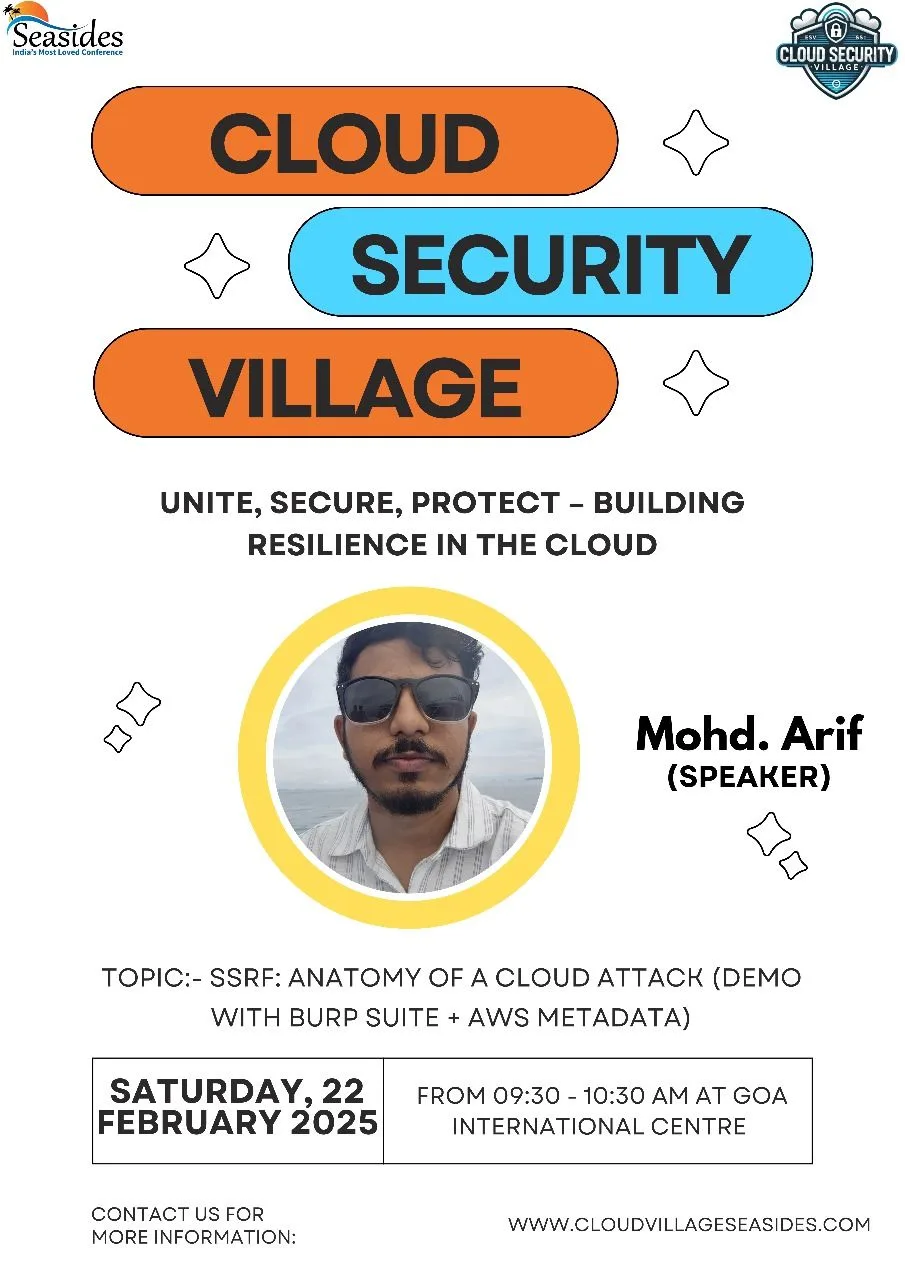
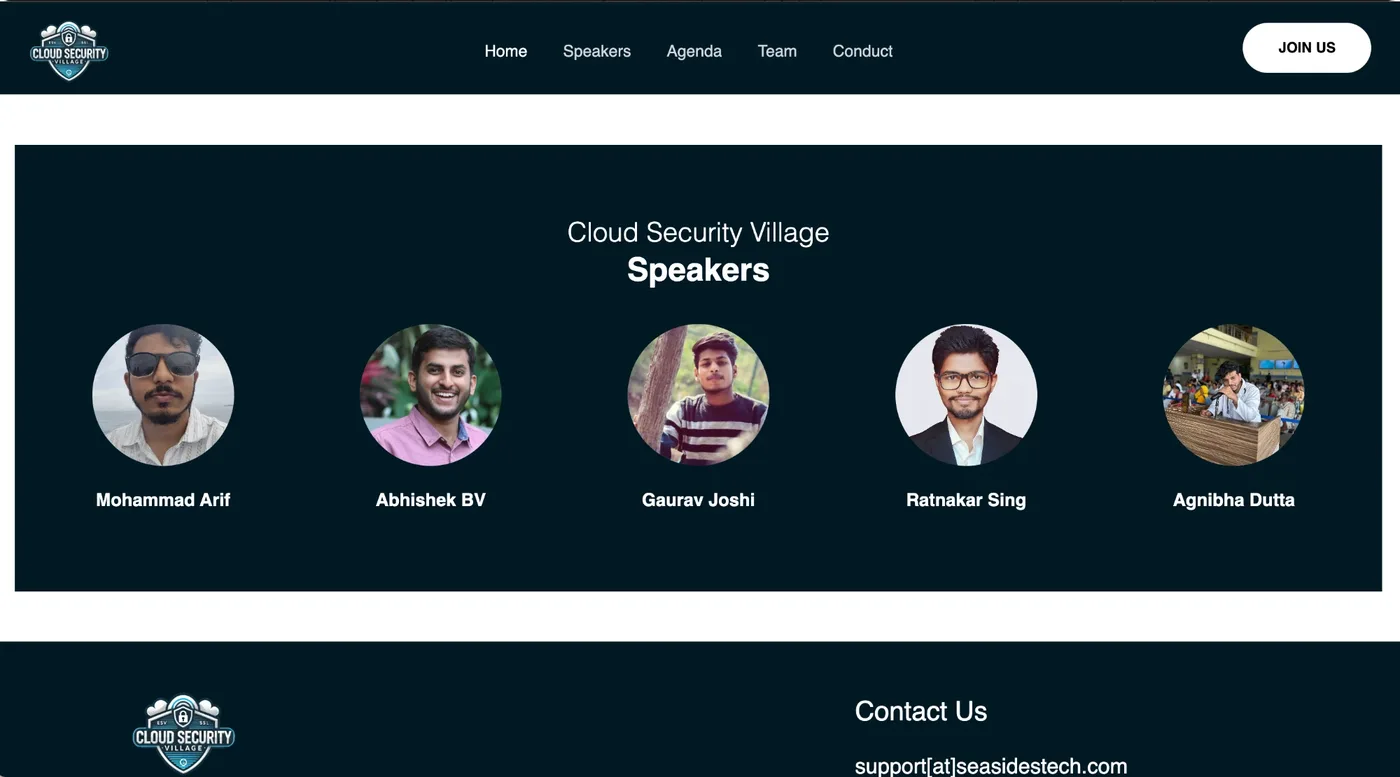
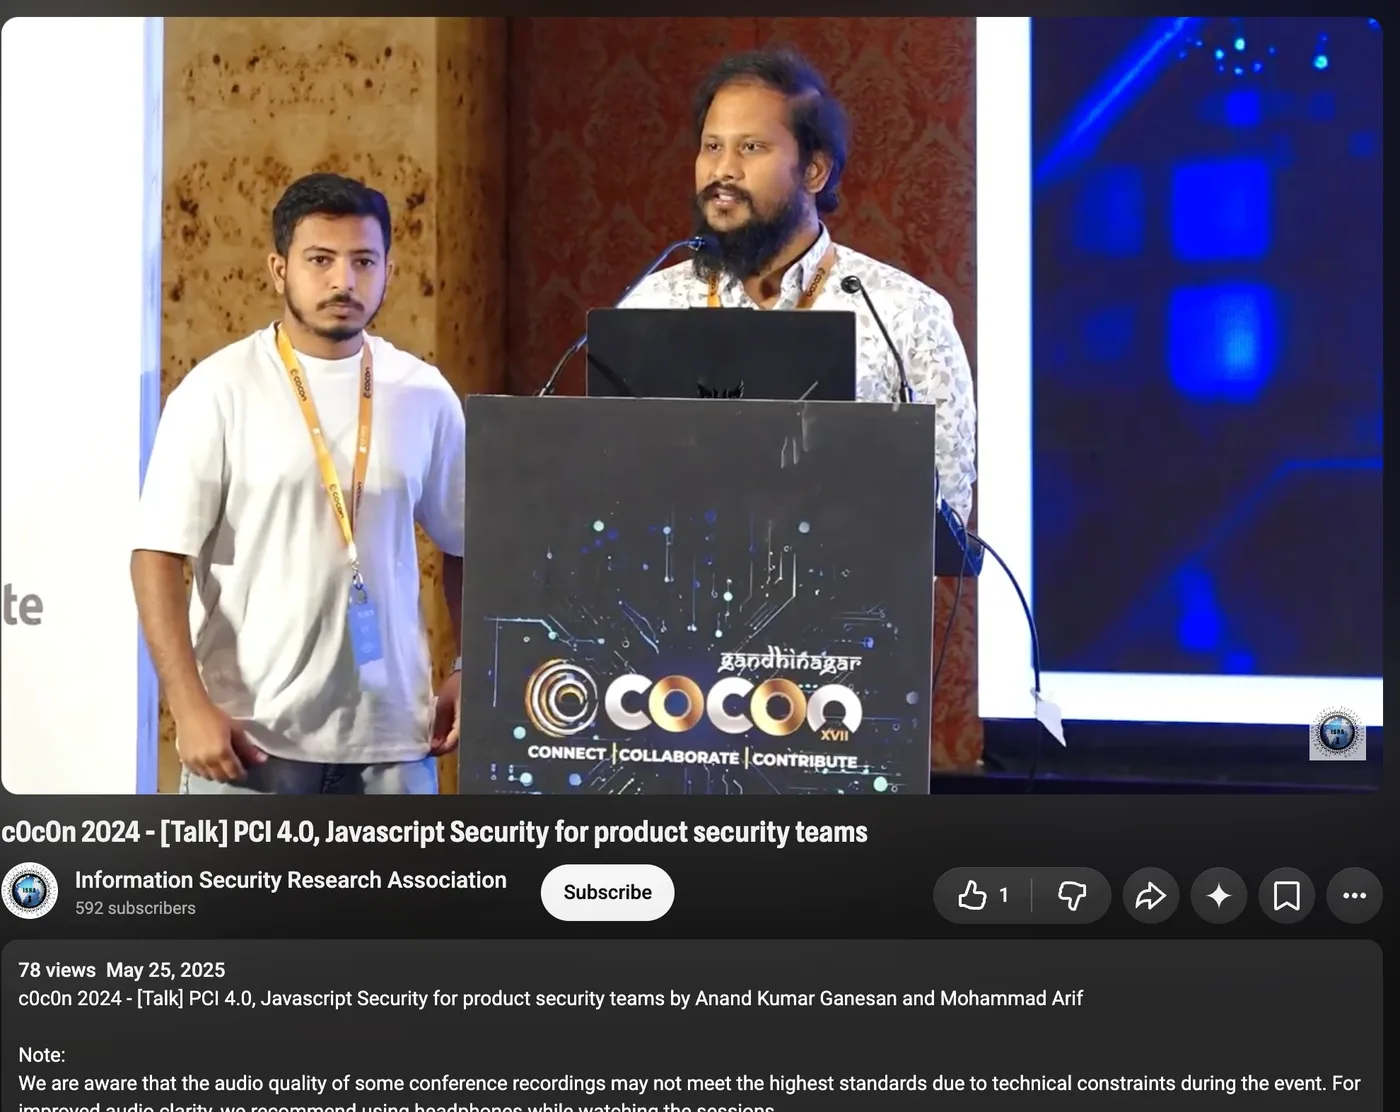
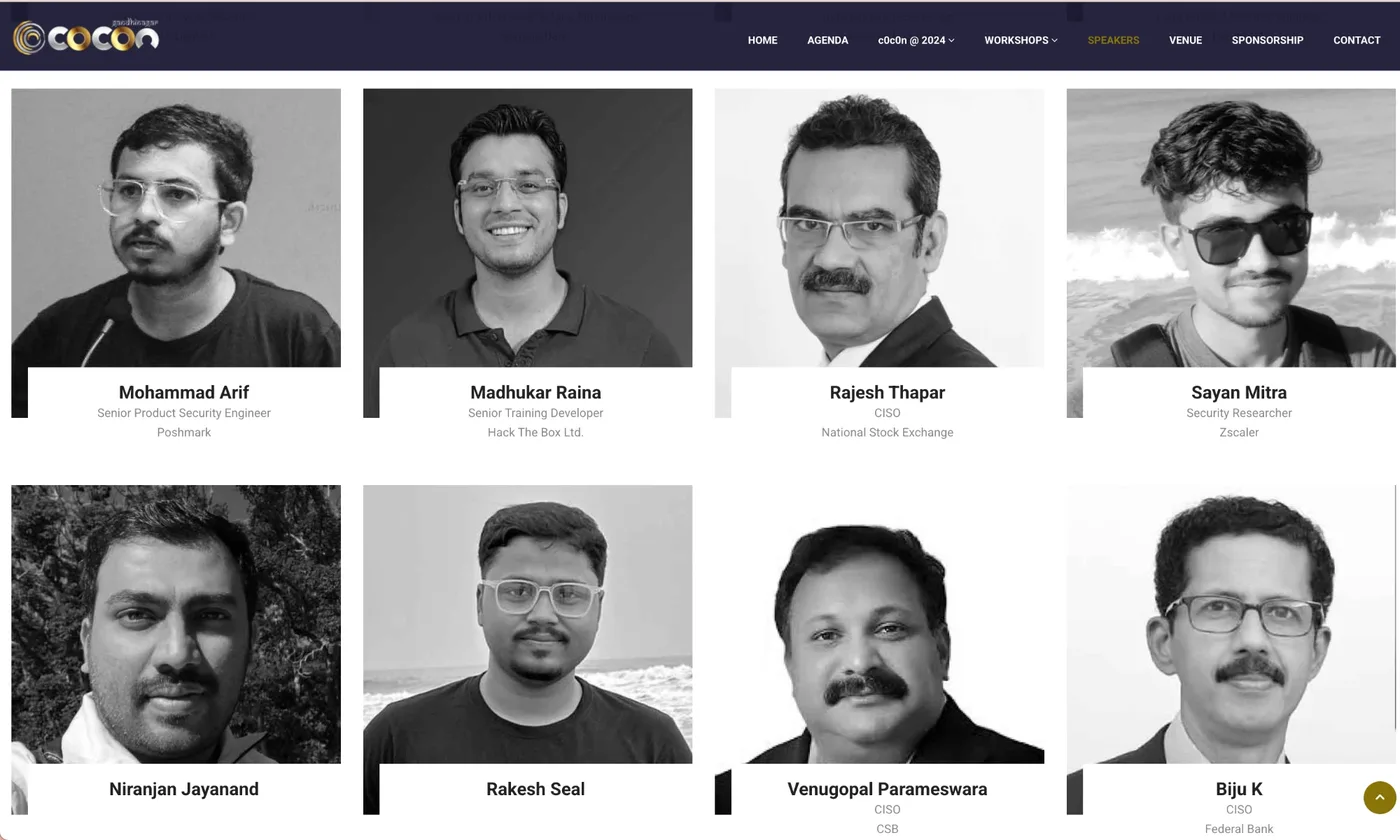
📸 Receipts (8)
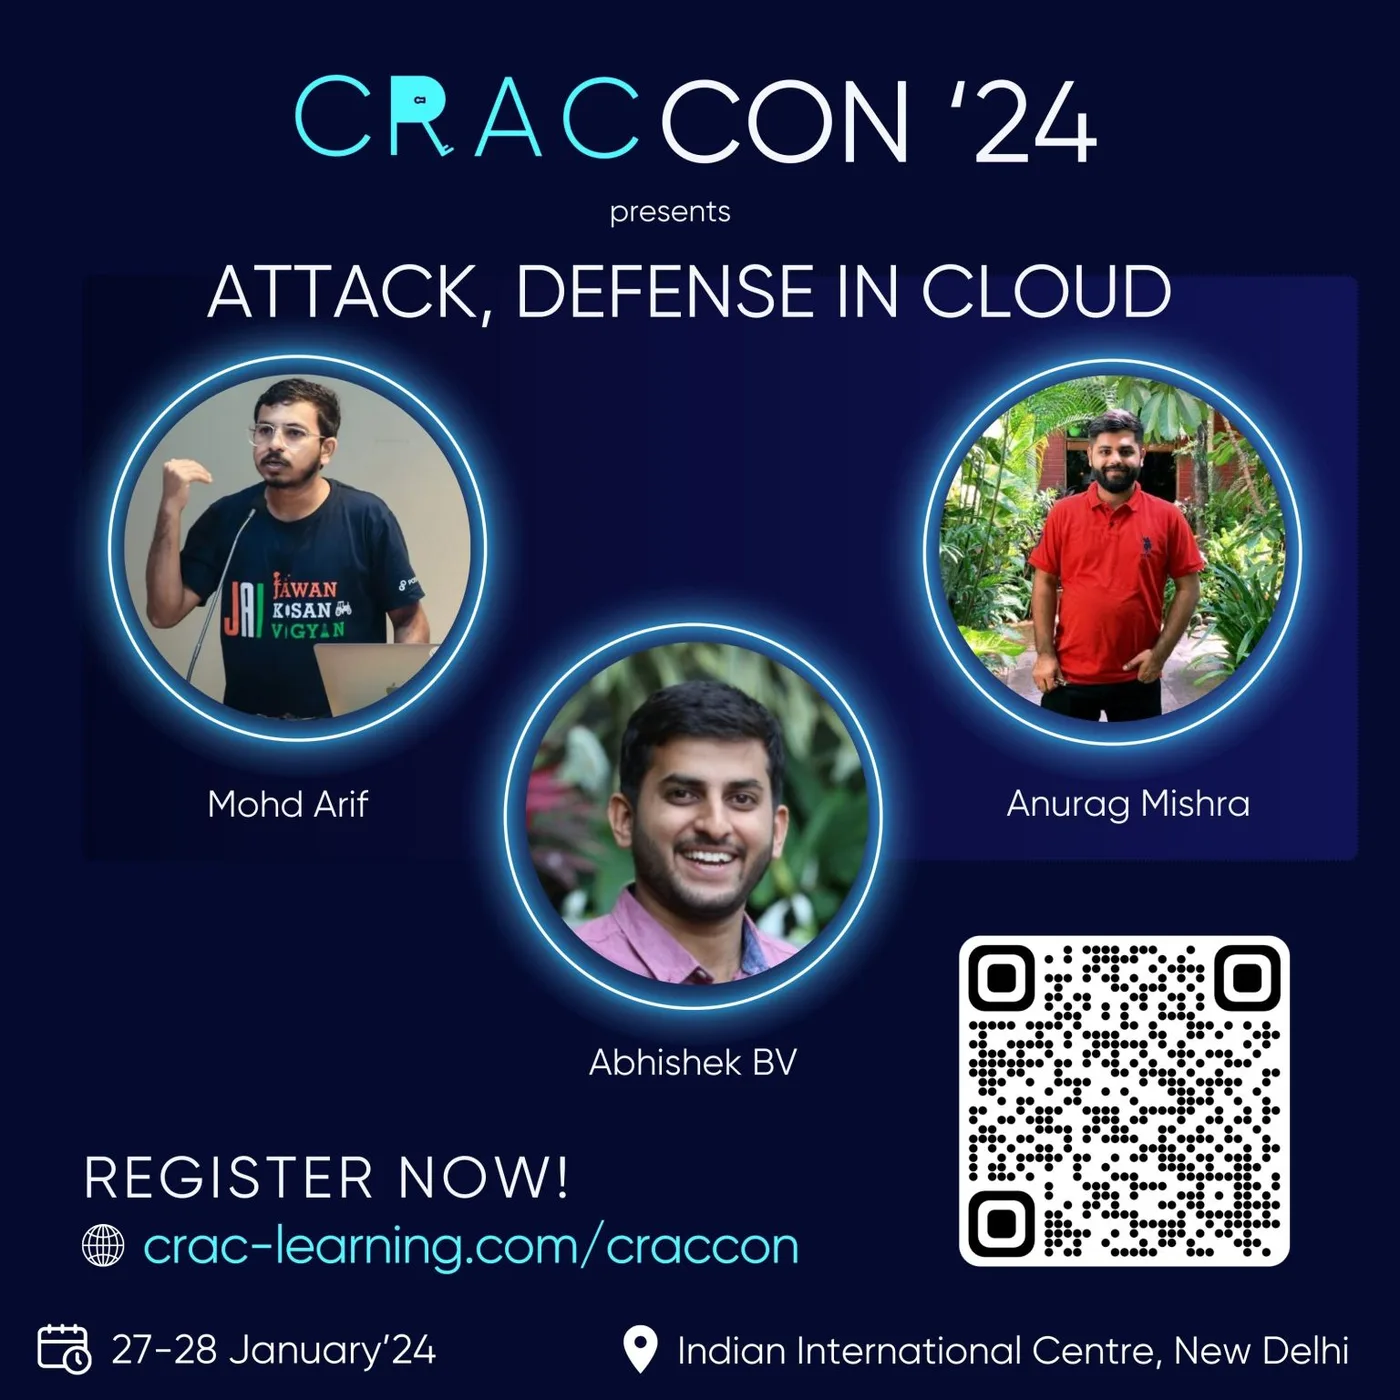 CRACCON '24 poster: Attack, Defense in Cloud, with Mohd Arif
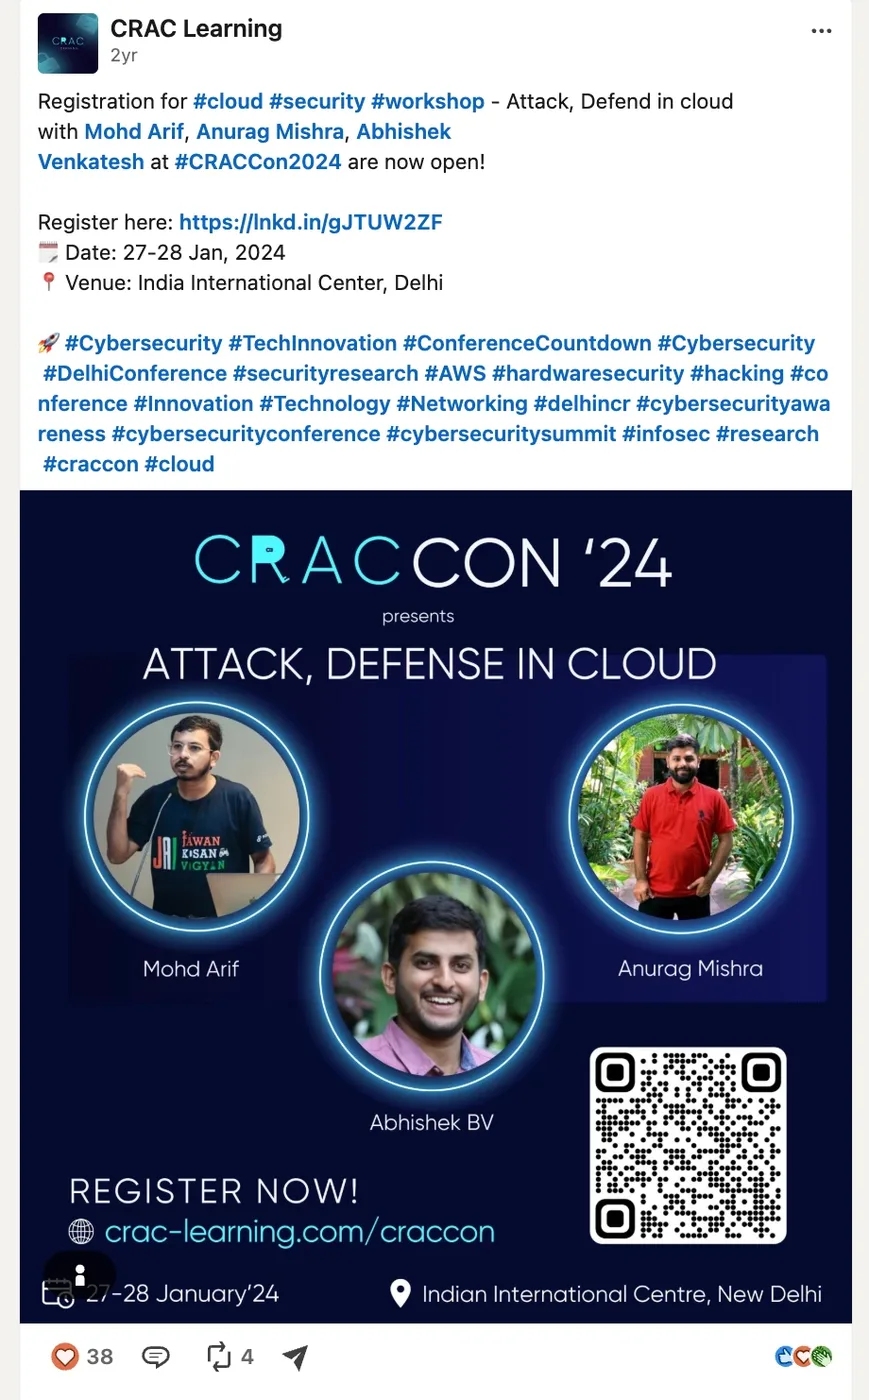 CRAC Learning registration announcement, 27-28 Jan 2024
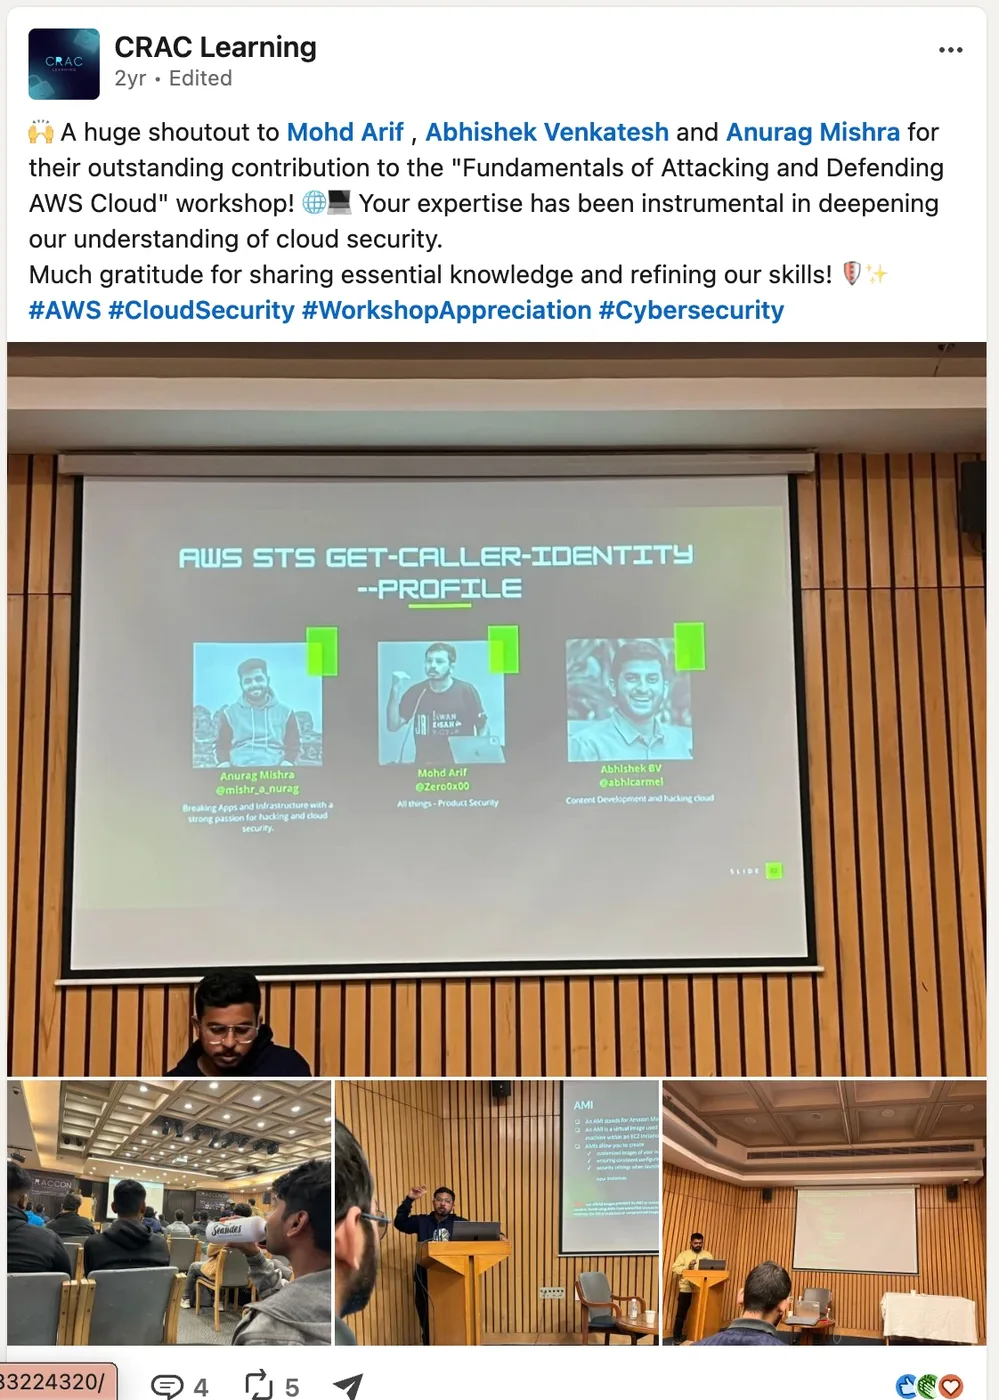 CRAC Learning post thanking the trainers
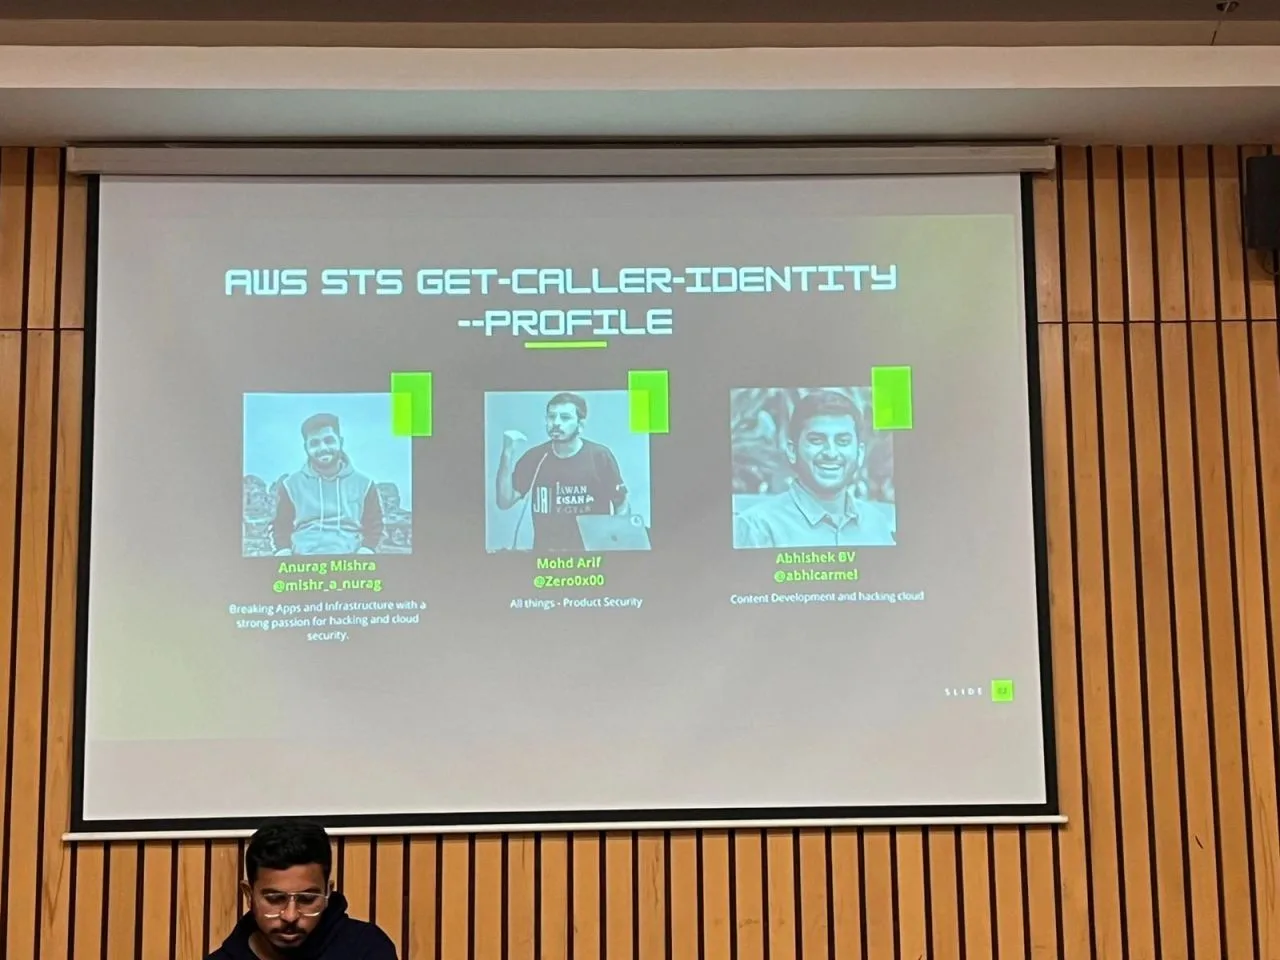 Workshop slide introducing the three trainers
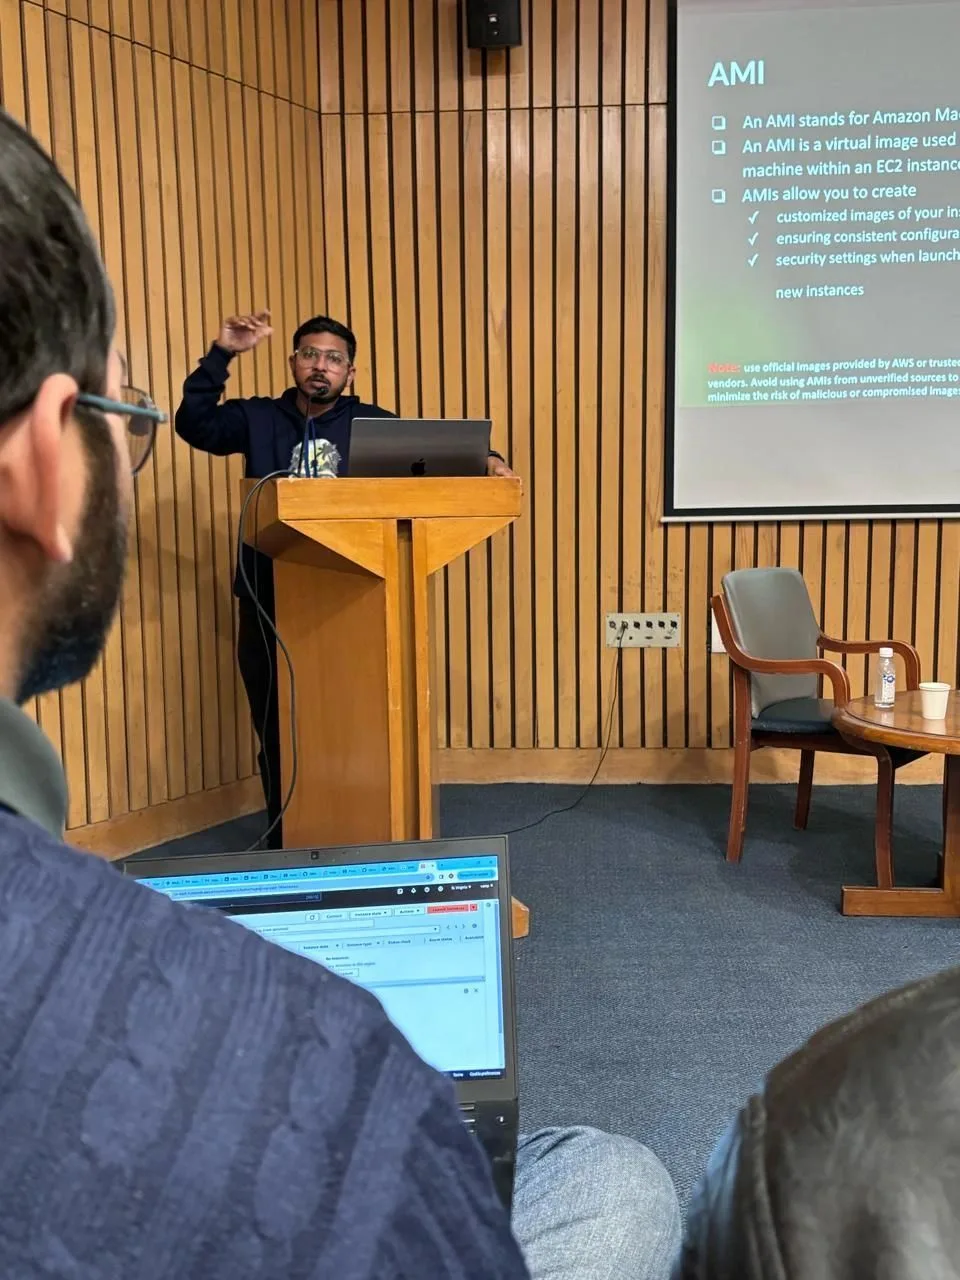 Delivering the AMI/EC2 session at CRACCON '24
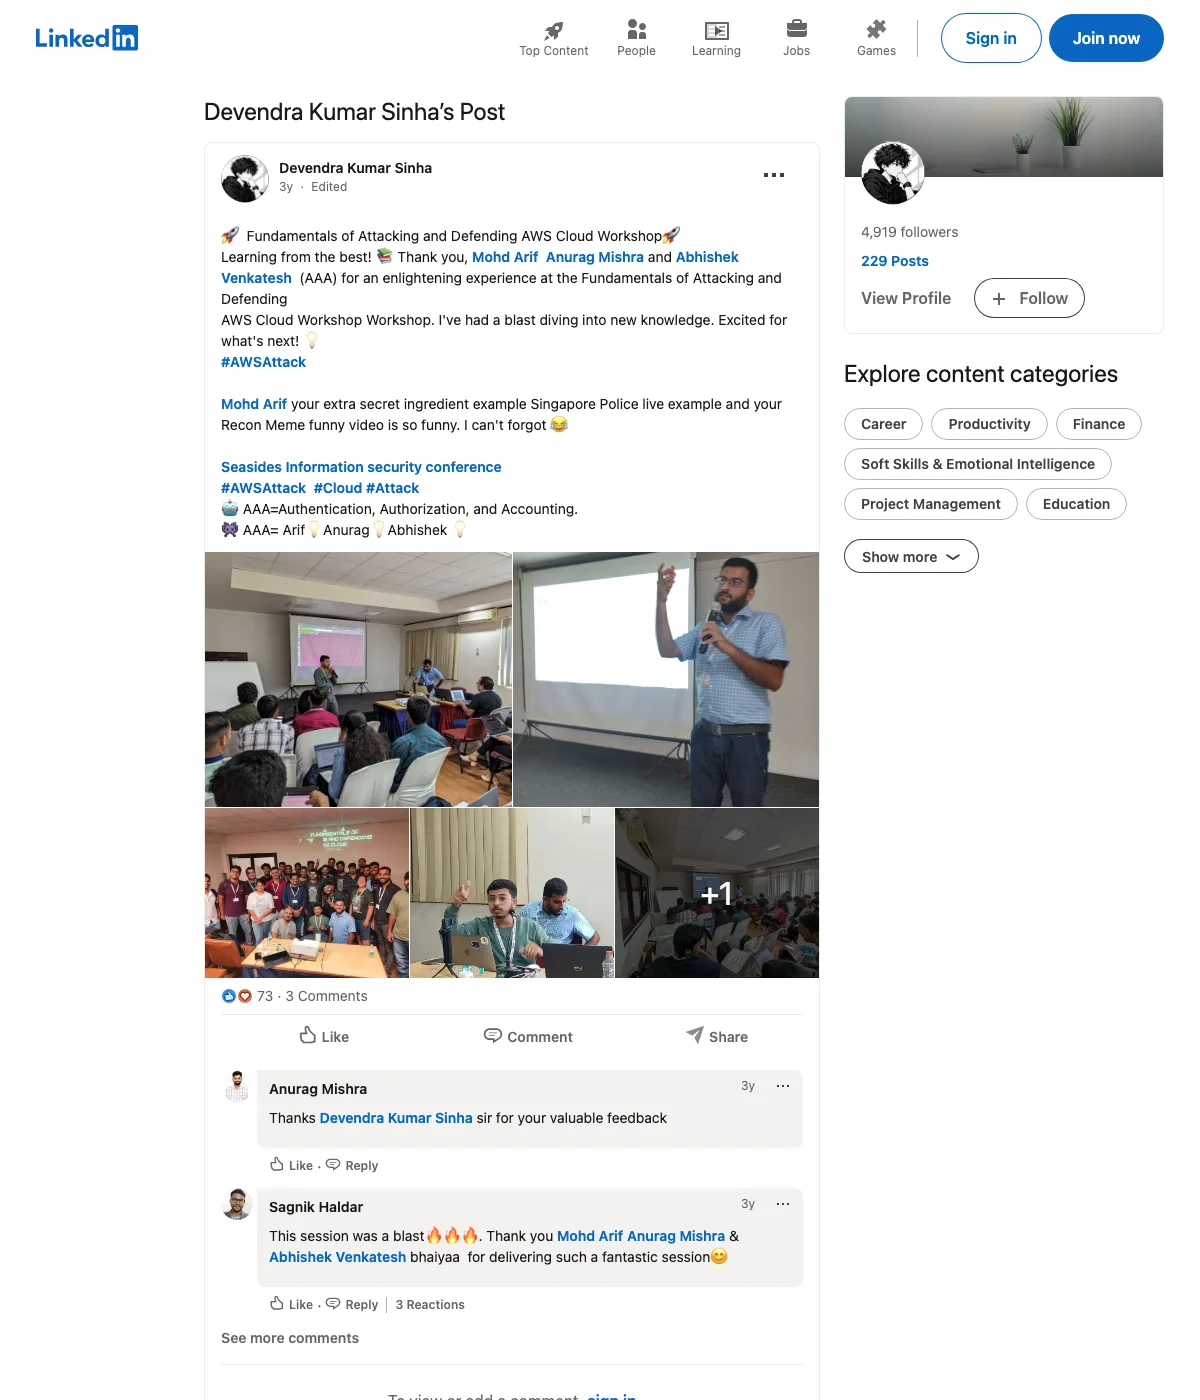 Attendee post thanking trainers, Seasides AWS workshop
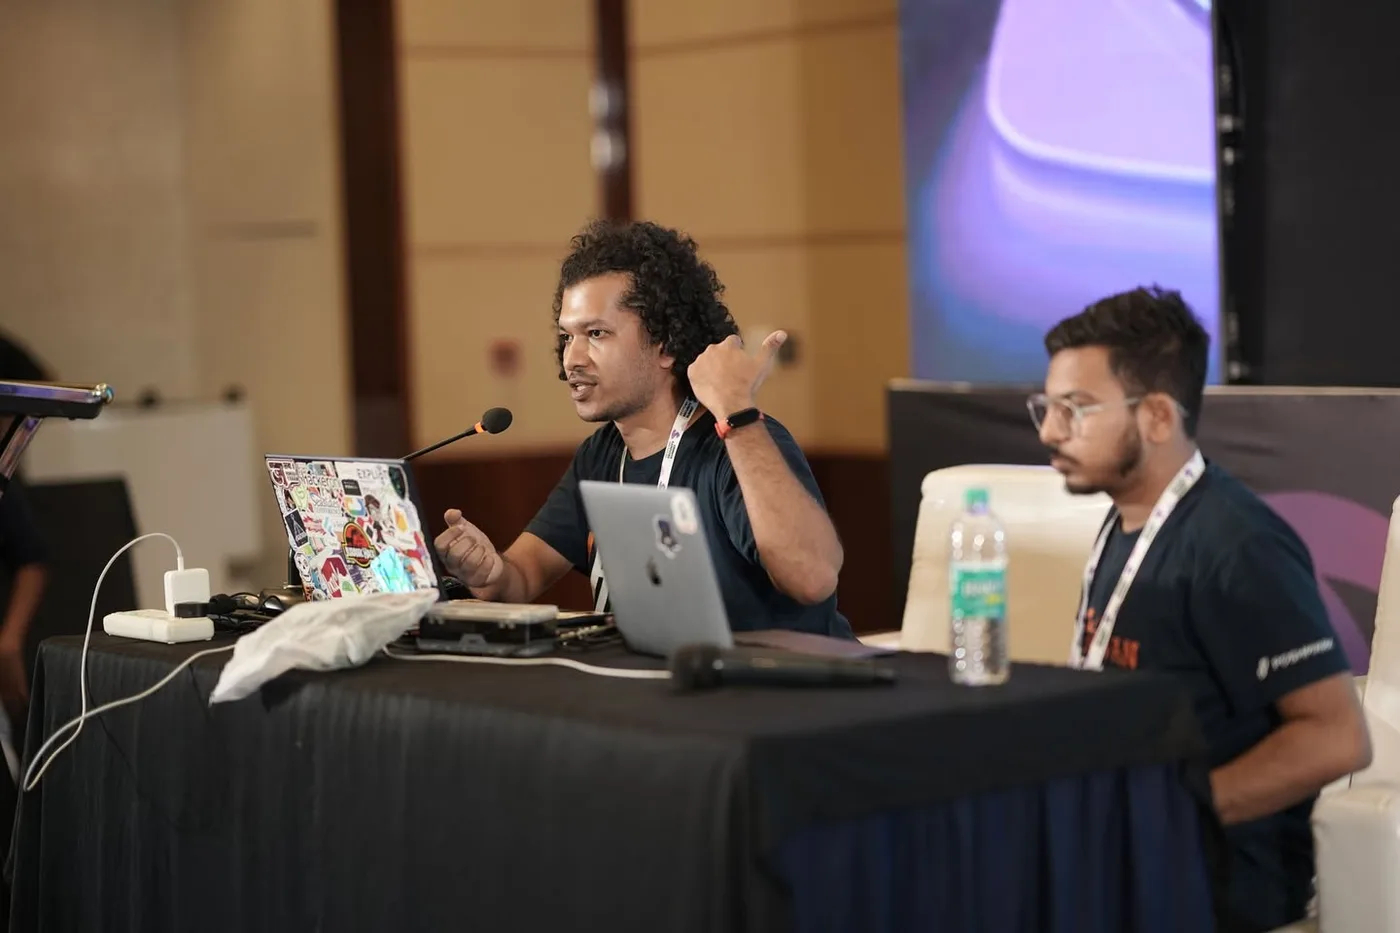
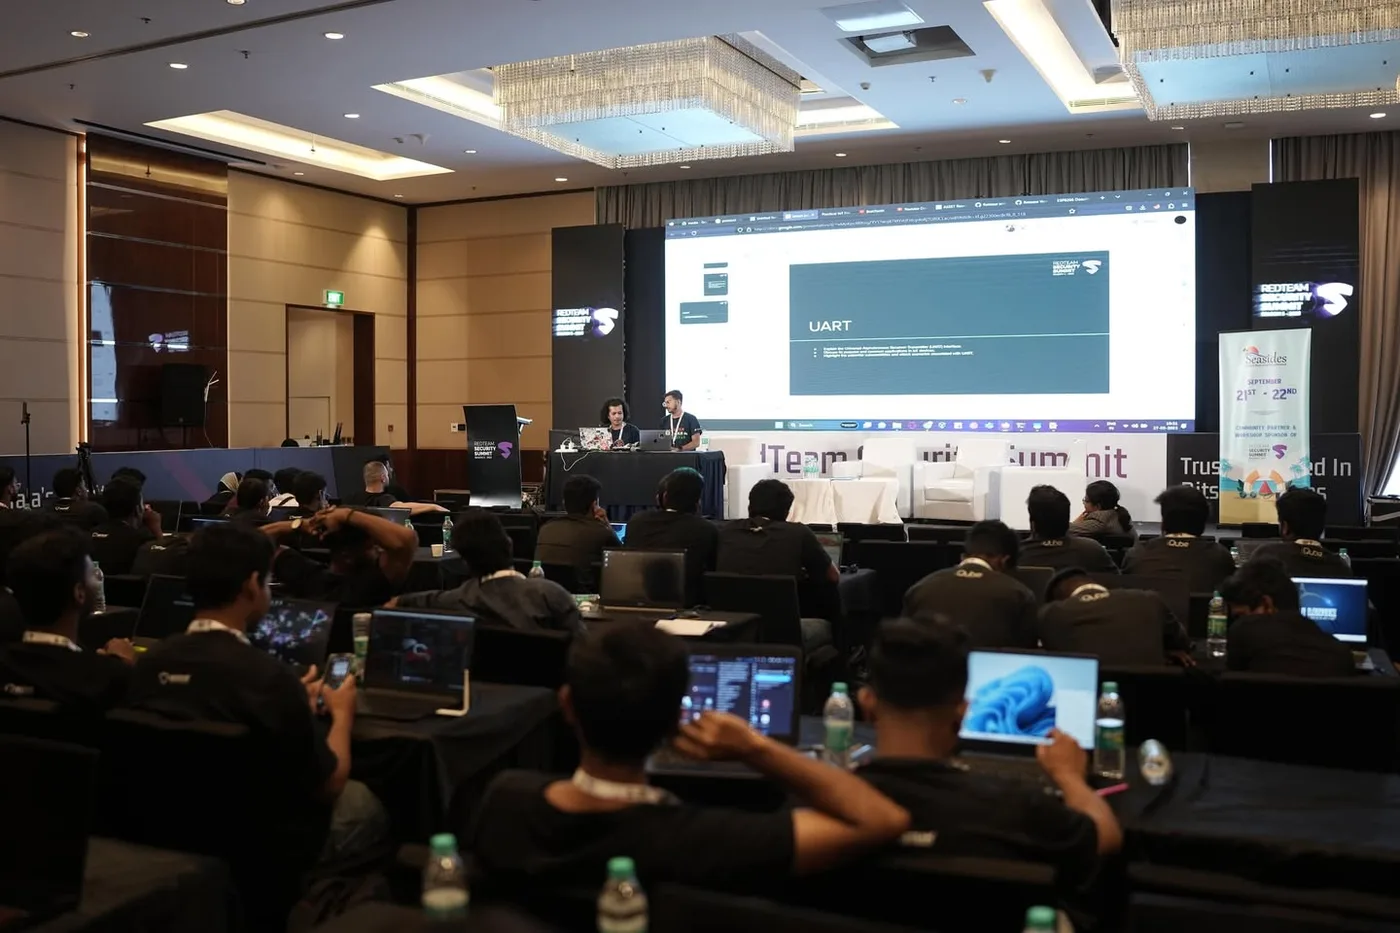
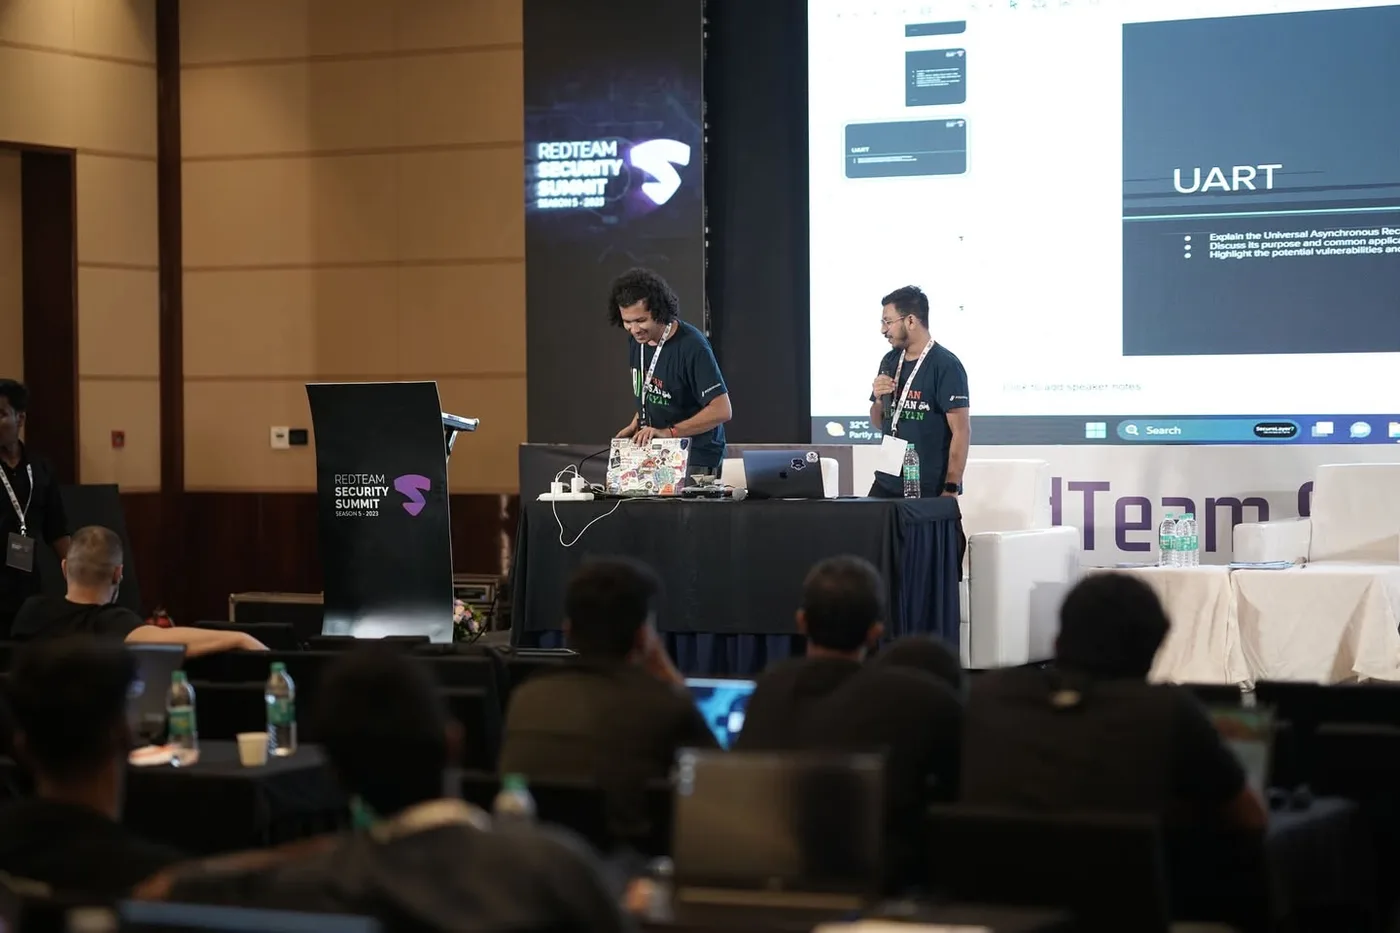
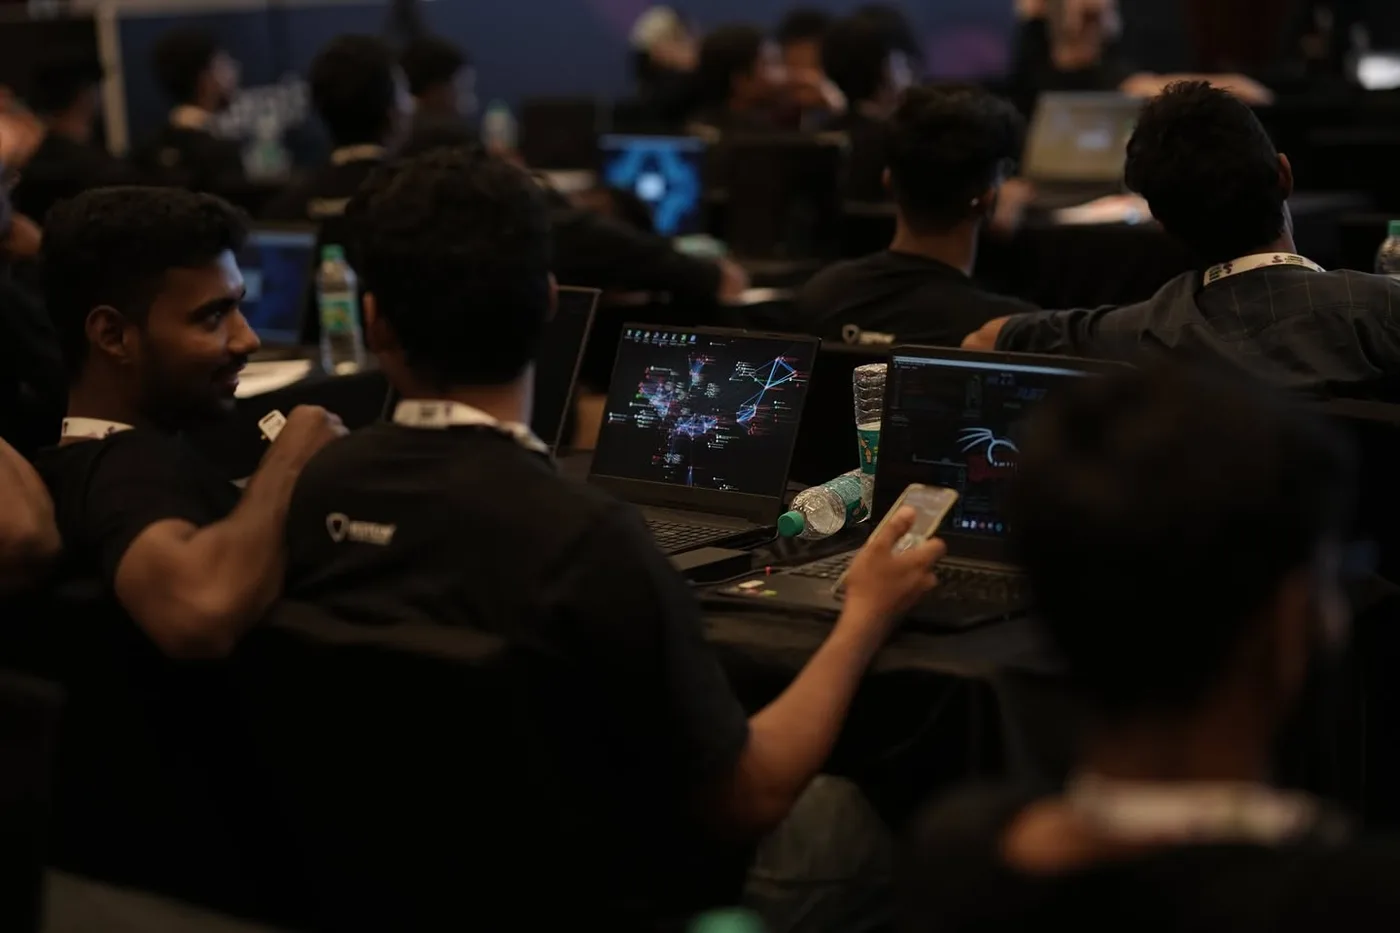
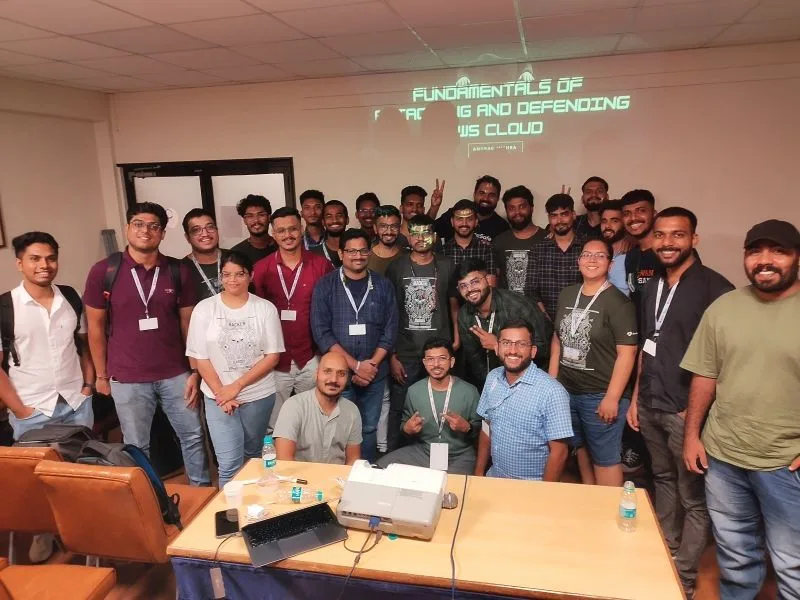 Seasides AWS workshop group photo
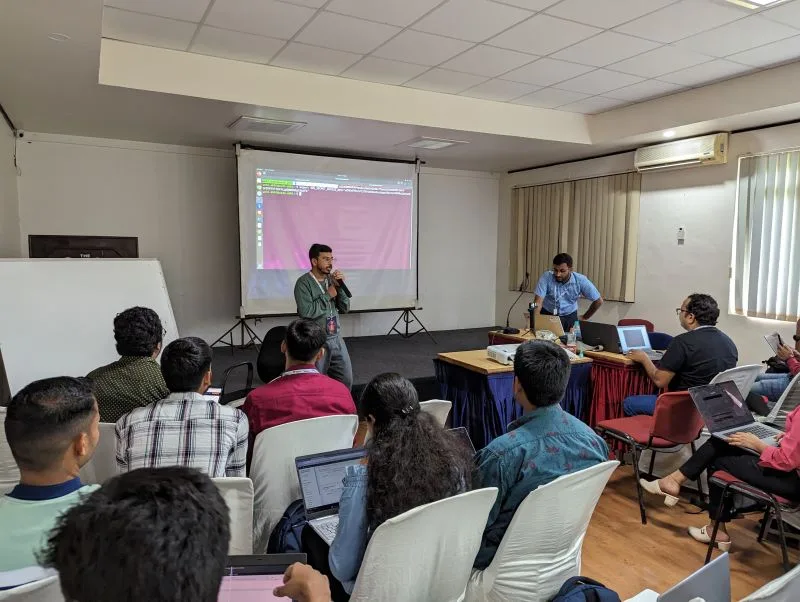 Seasides AWS workshop in session
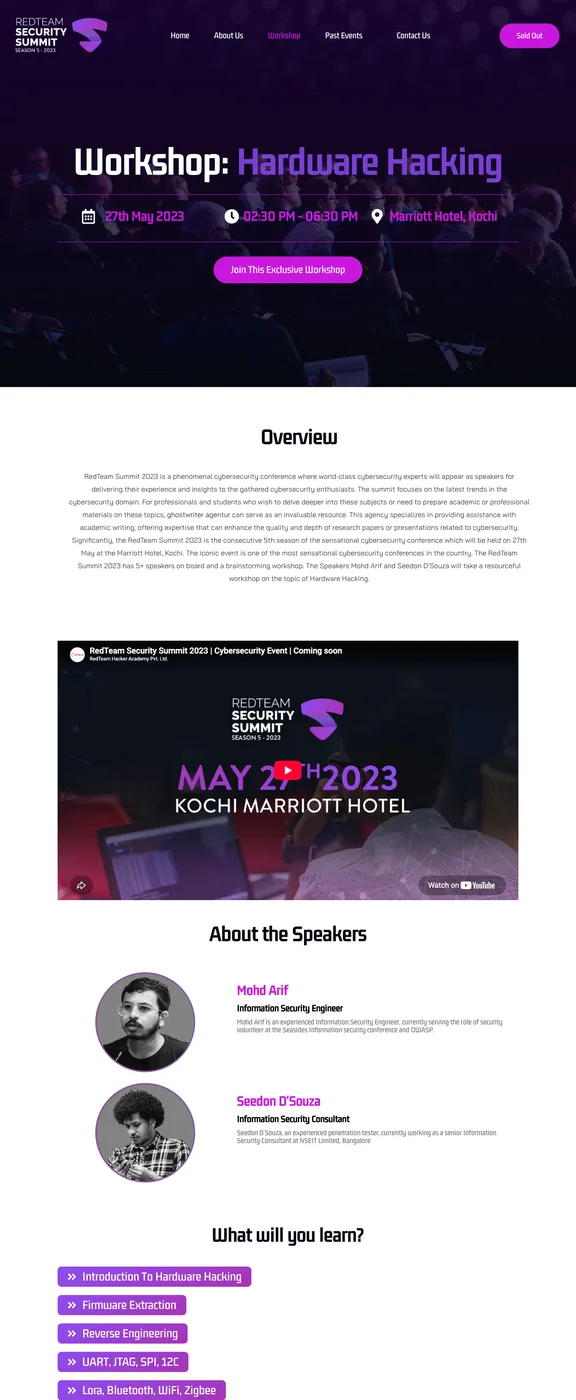
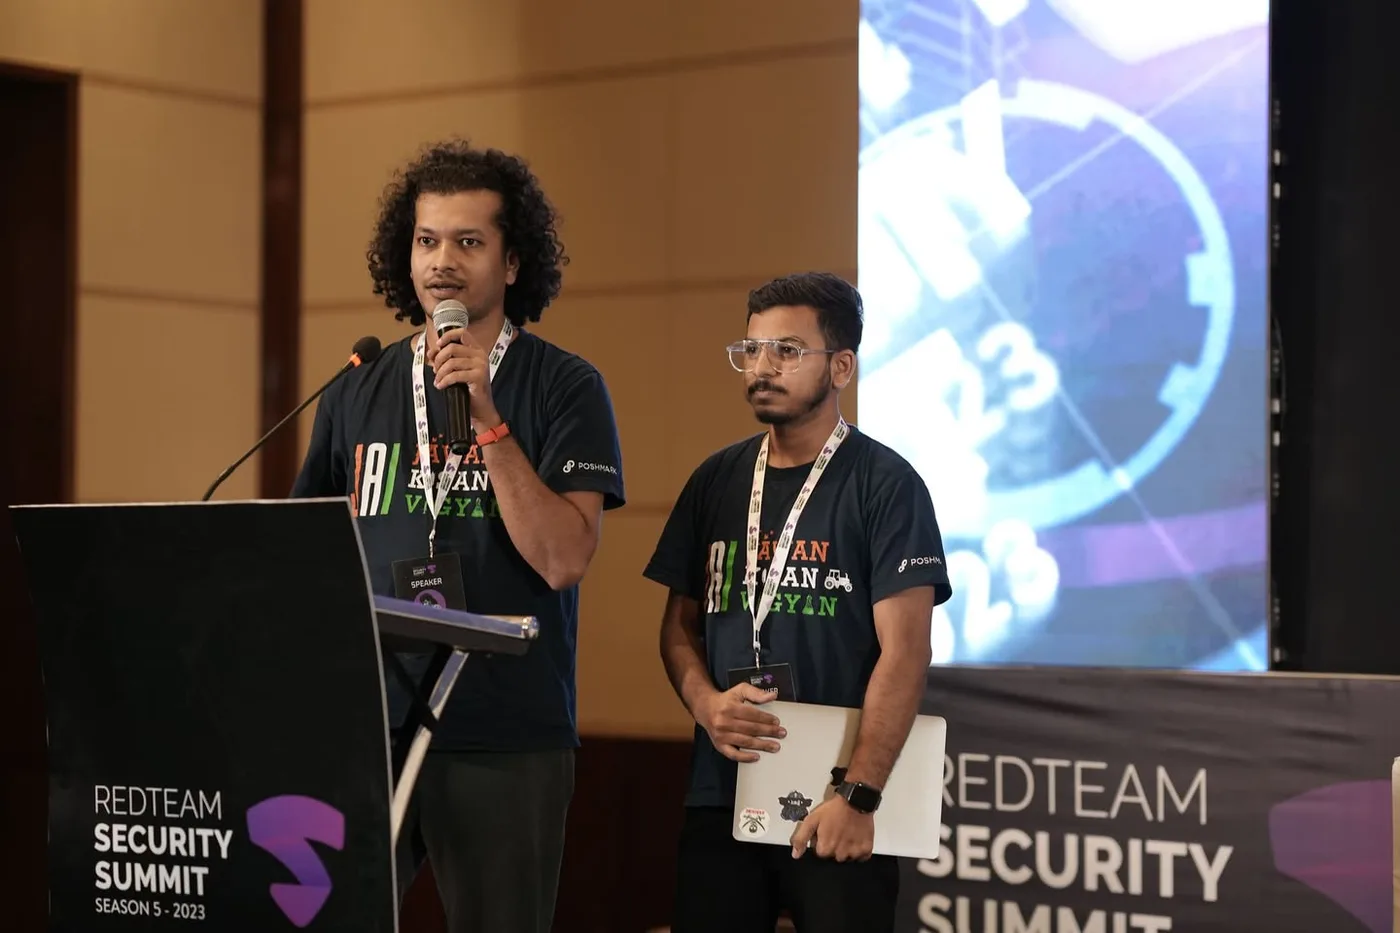
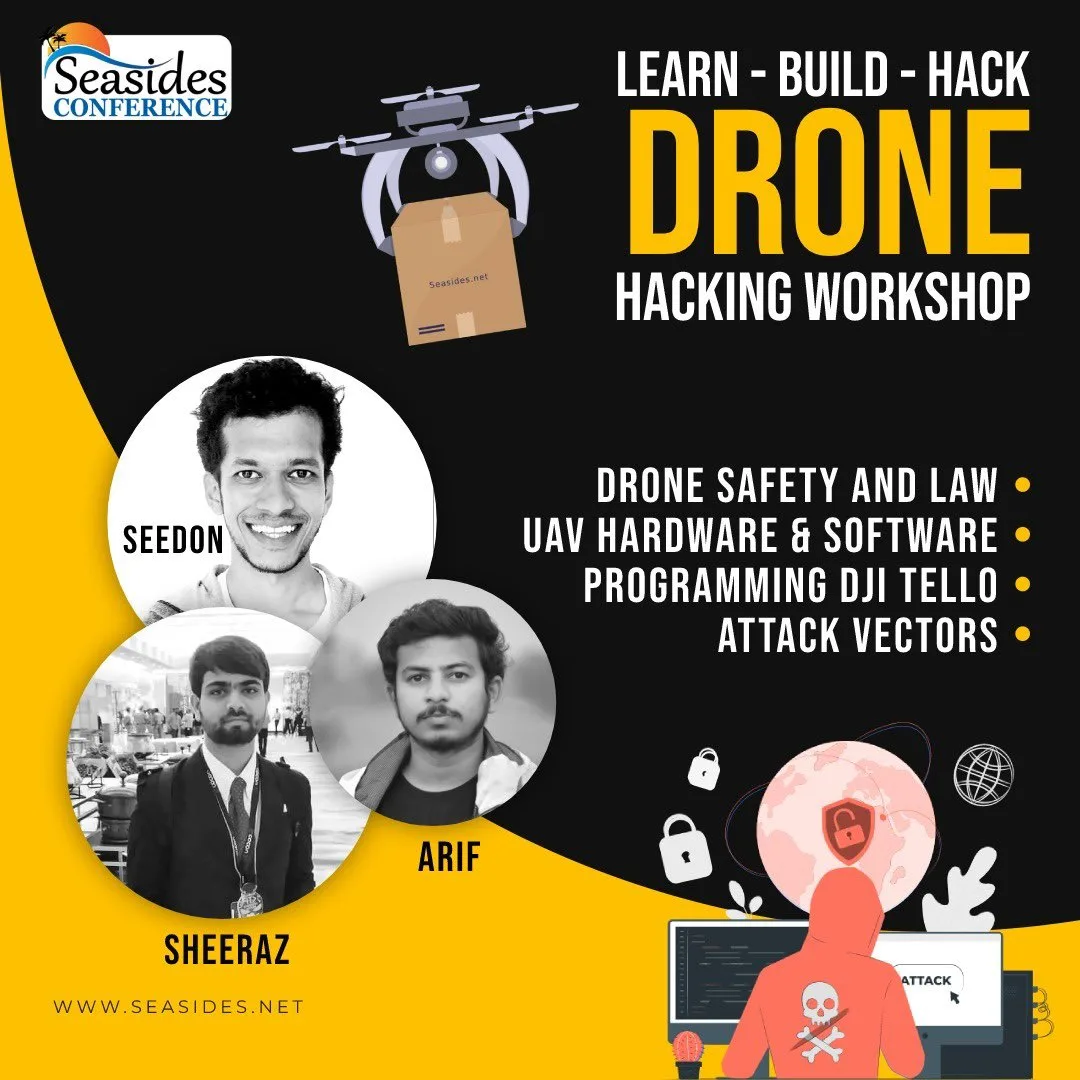
Community Leadership
• Core Team Member – Seasides Security Conference
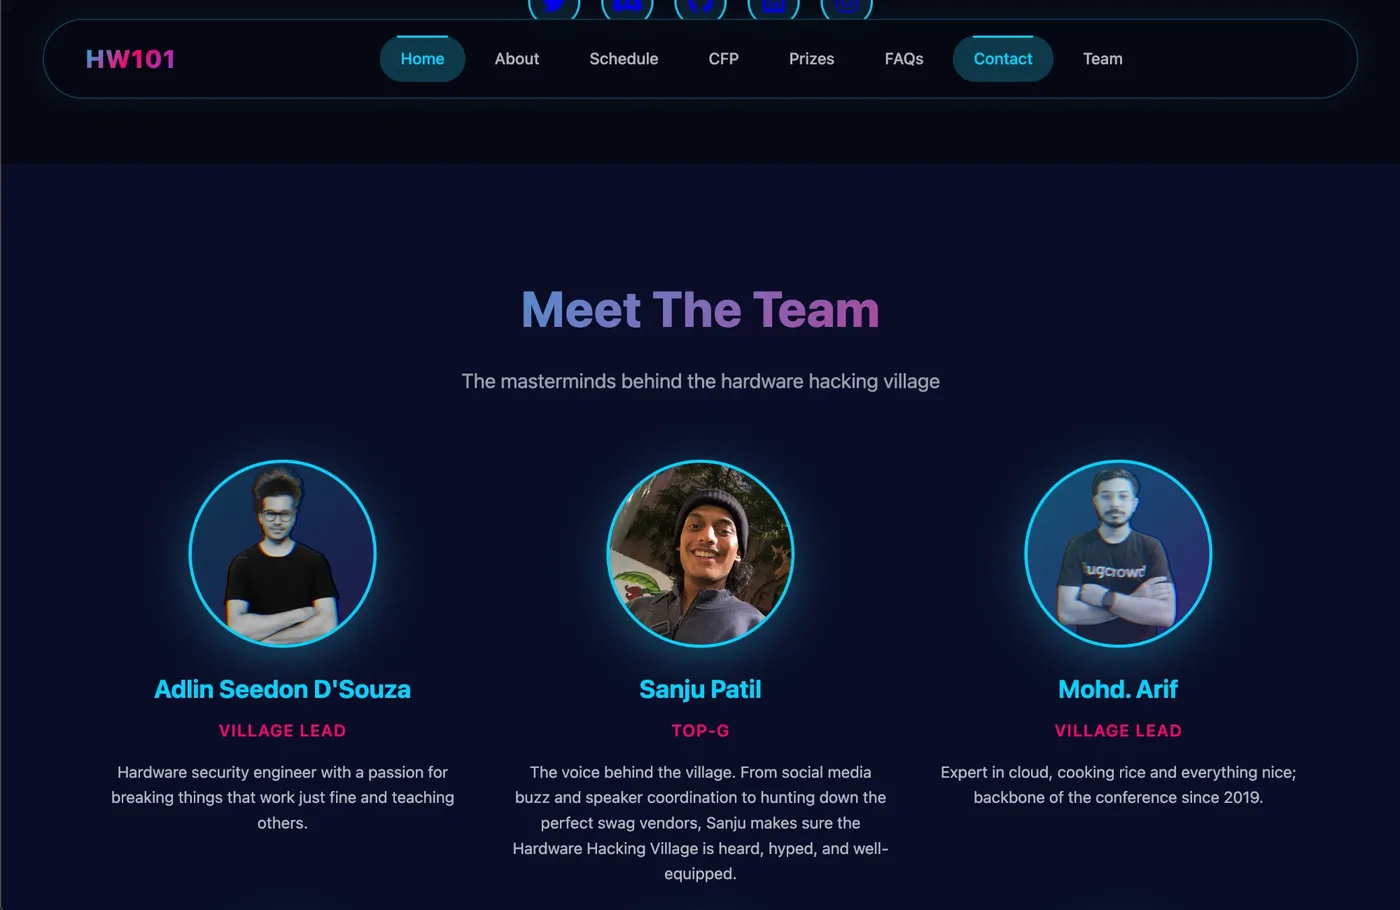
• Hardware Village Lead – Seasides (Hardware Security & Embedded Systems)
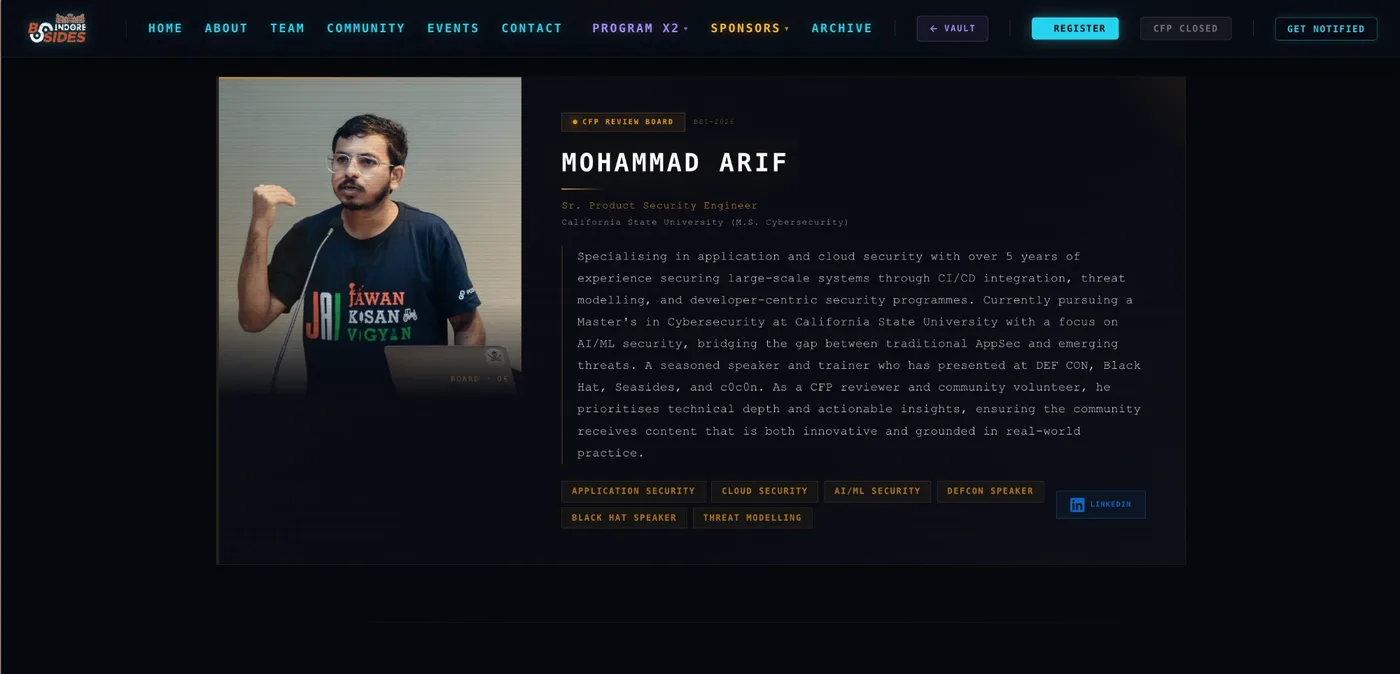
• CFP Review Board Member – BSides Indore 2026 (double-blind talk review) – board page
• Active contributor to global security communities including OWASP & BSides
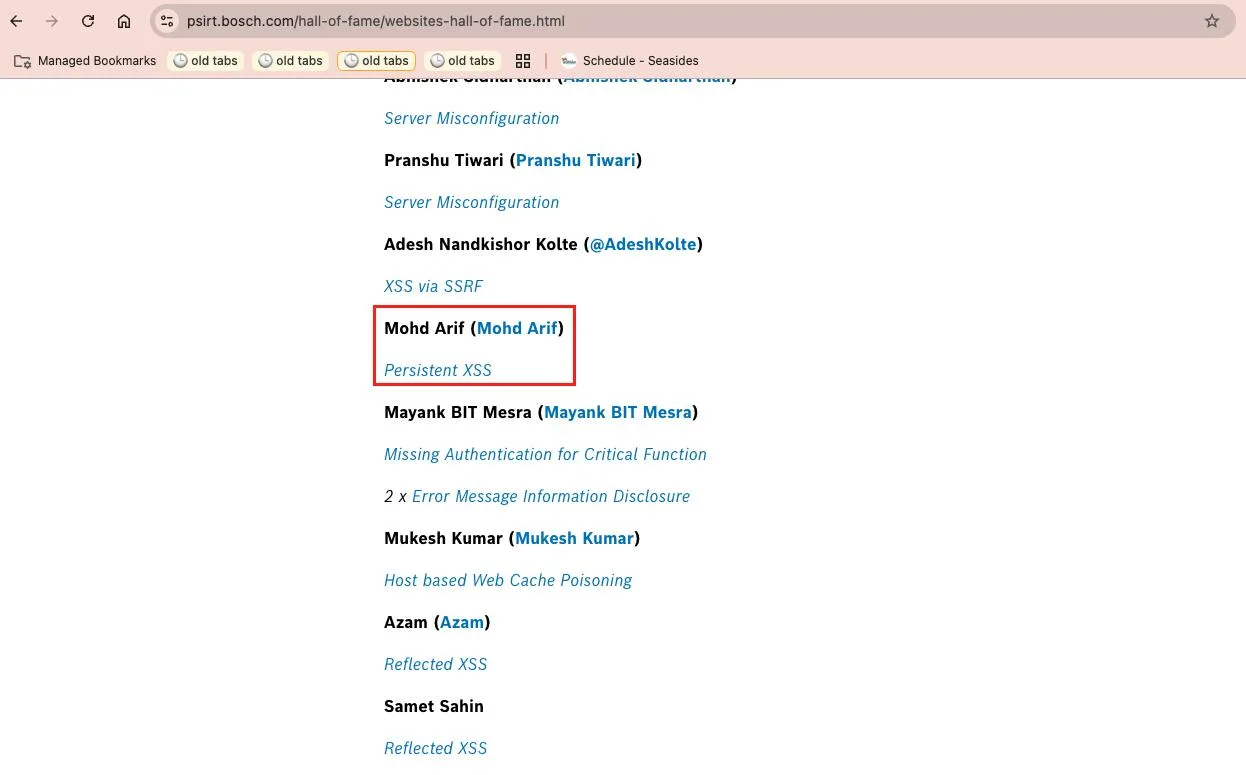
Awards & recognition
Recognition earned through execution, consistency, and contribution to the broader security ecosystem.
📸 Receipts (1)
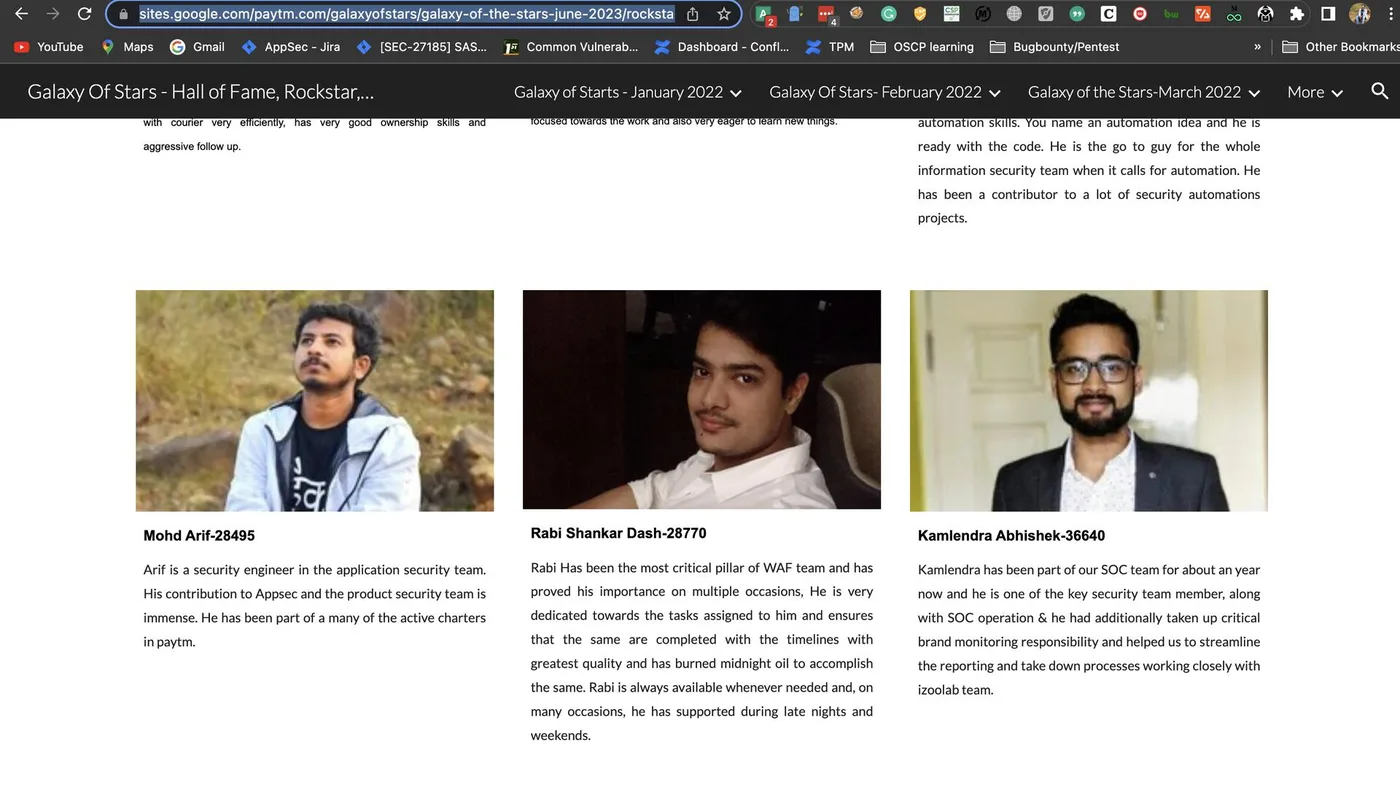
📸 Receipts (1)
Let’s build secure products that scale.
I’m especially well suited for roles in product security, application security, cloud security, security engineering, and AI/ML security, bringing a practical engineering foundation with growing specialization in secure AI systems.